Exposure management is a continuous, risk-based cybersecurity approach that involves identifying, prioritizing, and mitigating vulnerabilities, misconfigurations, excessive permissions, and other weaknesses that attackers are most likely to exploit across your IT infrastructure.
Also known as threat exposure management or cyber exposure management, this approach helps your security team focus on the conditions that pose the most risk to critical systems, sensitive data, and business operations.
How exposure management works
An effective exposure management program continuously discovers potential weaknesses, provides the context needed to understand their real-world impact, and helps teams act on the most urgent risks first.
A typical exposure management workflow includes the following steps:
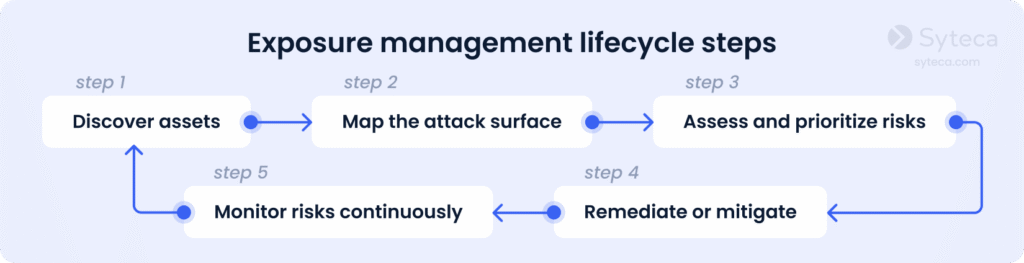
1. Discover assets
To start, your organization needs to perform a current inventory of the assets within your environments. Unknown or unmanaged assets can create blind spots that attackers may exploit.
Assets to discover for exposure management
Servers and virtual machines
Privileged and service accounts
Databases and data stores
Third-party services and APIs
2. Map the attack surface
After identifying assets, your security team should examine how attackers could reach them. This can become possible through publicly exposed services, vulnerable applications, weak credentials and configuration, excessive permissions, and insecure connections between systems.
3. Assess and prioritize risks
Not every risk deserves the same response, so risks should be prioritized. Your teams should evaluate the following:
- Exploitability
- Internet exposure
- Known threat activity
- Asset criticality
- Identity privileges
- Available security controls
- Potential business impact
Note that a lower-severity issue on a critical system may pose more risk than a high-severity issue on an isolated asset. This is because a weakness in a critical system can give attackers access to valuable data or disrupt important business operations, while a more severe issue on an isolated asset may cause little harm.
4. Remediate or mitigate
Depending on the exposure, remediation steps may involve applying a patch, changing a configuration, removing unnecessary public access, disabling an unused service, restricting permissions, or enforcing stronger authentication. When an immediate fix isn’t possible, apply compensating controls to reduce risk.
5. Monitor risks continuously
Environments change constantly as your organization deploys new applications, adds cloud resources, changes user permissions, and onboards third parties. Make sure your team detects new exposures before they become entry points for attackers. Also, it’s vital to track remediation progress and validate that fixes work.
Expert tip:
Attack path analysis improves this process by showing how separate weaknesses can combine. For example, an attacker could exploit an internet-facing flaw, use a compromised account to access another system, and then exploit excessive privileges to access your sensitive data.
Cloud security platforms similarly describe exposure findings as correlated signals involving vulnerabilities, configurations, threats, and resource relationships, not simply isolated issues.
Exposure management vs. vulnerability management
The difference between vulnerability management vs. exposure management is context. Vulnerability management asks, “What is vulnerable?” It identifies and helps remediate software flaws, missing patches, and insecure configurations. Exposure management asks, “What actually puts us at risk?” by adding business context, attack paths, identity risk, asset value, and likely attacker behavior to the vulnerability list.
Vulnerability management remains an essential security practice. However, a high number of findings can make it difficult to determine which issues need immediate attention. Exposure management helps teams focus on the vulnerabilities and related conditions that could realistically lead to material impact.
Why exposure management matters
Modern IT environments are complex and distributed. Therefore, your organization may not have complete visibility into all the assets and environments you need to protect. Exposure management helps turn this complexity into a clearer, business-focused view of cyber risks.
Exposure management key benefits
Reveal likely attack paths
Teams can address the exposures attackers are most likely to exploit rather than respond to findings in arbitrary order.
Business context helps security teams avoid treating every known vulnerability or configuration issue as equally urgent.
Security leaders can explain cyber risk to executives and the board in terms of critical assets, potential impact, remediation status, and business priorities.
Exposure management best practices
Exposure management is most effective when discovery, prioritization, remediation, and validation continuously work together. These practices can help your security teams focus on the exposures most likely to affect critical assets and business operations.
5 best practices for efficient exposure management
1
Maintain complete asset visibility
2
Prioritize by exploitability and business context
3
Automate discovery and low-risk remediation
4
Align with applicable compliance requirements
5
Reduce privileged access exposure
1. Maintain complete asset visibility
You cannot reduce exposure you cannot see, so maintain an up-to-date inventory of systems, cloud resources, applications, identities, services, and external connections. NIST Cybersecurity Framework 2.0 [PDF] emphasizes identifying and managing assets according to their importance to organizational objectives and risk strategy.
2. Prioritize by exploitability and business context
Prioritize findings based on exploitability and business context, not Common Vulnerability Scoring System (CVSS) scores alone. Consider the following questions during prioritization:
- Is the asset externally reachable, or accessible through an internal attack path?
- Are there any actively exploited weaknesses for the asset?
- Does the affected asset support a critical business process or service?
- What data or systems could the asset expose if compromised?
- Does the affected identity have elevated permissions?
Answering these questions helps security teams direct remediation efforts toward exposures that pose the greatest risk to critical assets and business operations.
3. Automate discovery and low-risk remediation
Automate discovery and low-risk remediation where possible. Continuous scanning, configuration monitoring, and automated workflows can help teams identify changes quickly and reduce the time between detection and mitigation. CISA also recommends regularly assessing internet exposure and reducing unnecessary public access.
4. Align with applicable compliance requirements
Align the program with applicable compliance requirements, such as NIS2, DORA, and PCI DSS. Exposure management does not automatically make an organization compliant, but its asset inventory, risk prioritization, access control, remediation, monitoring, and evidence-gathering activities can support broader compliance efforts.
Compliance requirements to align with your exposure management program
5. Reduce privileged access exposure
Unmanaged privileged accounts and excessive permissions are among the highest-impact exposures because they can allow an attacker to turn an initial foothold into access to critical systems. Privileged access management (PAM), account discovery, and regular user access reviews help organizations reduce this identity-related risk through stronger access control, visibility, and ongoing oversight.
Syteca is an inside security platform that can enhance your organization’s exposure management efforts. Syteca’s privileged access management, session monitoring, identity threat detection and response (ITDR), and endpoint risk and compliance control (ERCC) provide a holistic approach to your overall risk management, reducing the likelihood of a wide range of potential cyberattacks.
Want to try Syteca? Request access
to the online demo!
See why clients from 70+ countries already use Syteca.
FAQ
Exposure management is the ongoing process of identifying, prioritizing, and reducing security conditions that could give attackers access to your valuable assets. It considers vulnerabilities alongside factors such as reachability, misconfigurations, asset importance, identity privileges, and potential attack paths.
Vulnerability management identifies, assesses, and remediates known software flaws and insecure configurations. Exposure management builds on that work by adding context, including exploitability, internet reachability, critical asset value, identity permissions, and potential attack paths. This helps teams determine which weaknesses are most likely to create meaningful business risk.
Continuous threat exposure management is a structured, repeatable framework for operationalizing exposure-management activities. It typically includes scoping, discovery, prioritization, validation, and mobilization, helping organizations continuously reduce the exposures that pose the greatest risk.