Build Privilege Elevation rules that decide when a Windows application should Auto-elevate, require approval, or be denied. It includes targeting criteria, endpoints, users, and how conflicting rules resolve.
A Privilege Elevation rule defines what triggers it (which application, on which endpoints, for which users) and what happens when it does: Auto-elevate, Require approval, or Deny.
The Rules page
1
Open Privilege Elevation
Log in as a user with the Privilege Elevation administrative permission. In the left navigation click Privilege Elevation.
2
Select the Rules tab
The Rules tab shows every configured rule in a grid. It is empty by default until you create one.
Any Management Tool user with the Privilege Elevation administrative permission can create, edit, enable, disable, and delete any rule, regardless of who created it. There are no per-rule permissions and no rule owner.
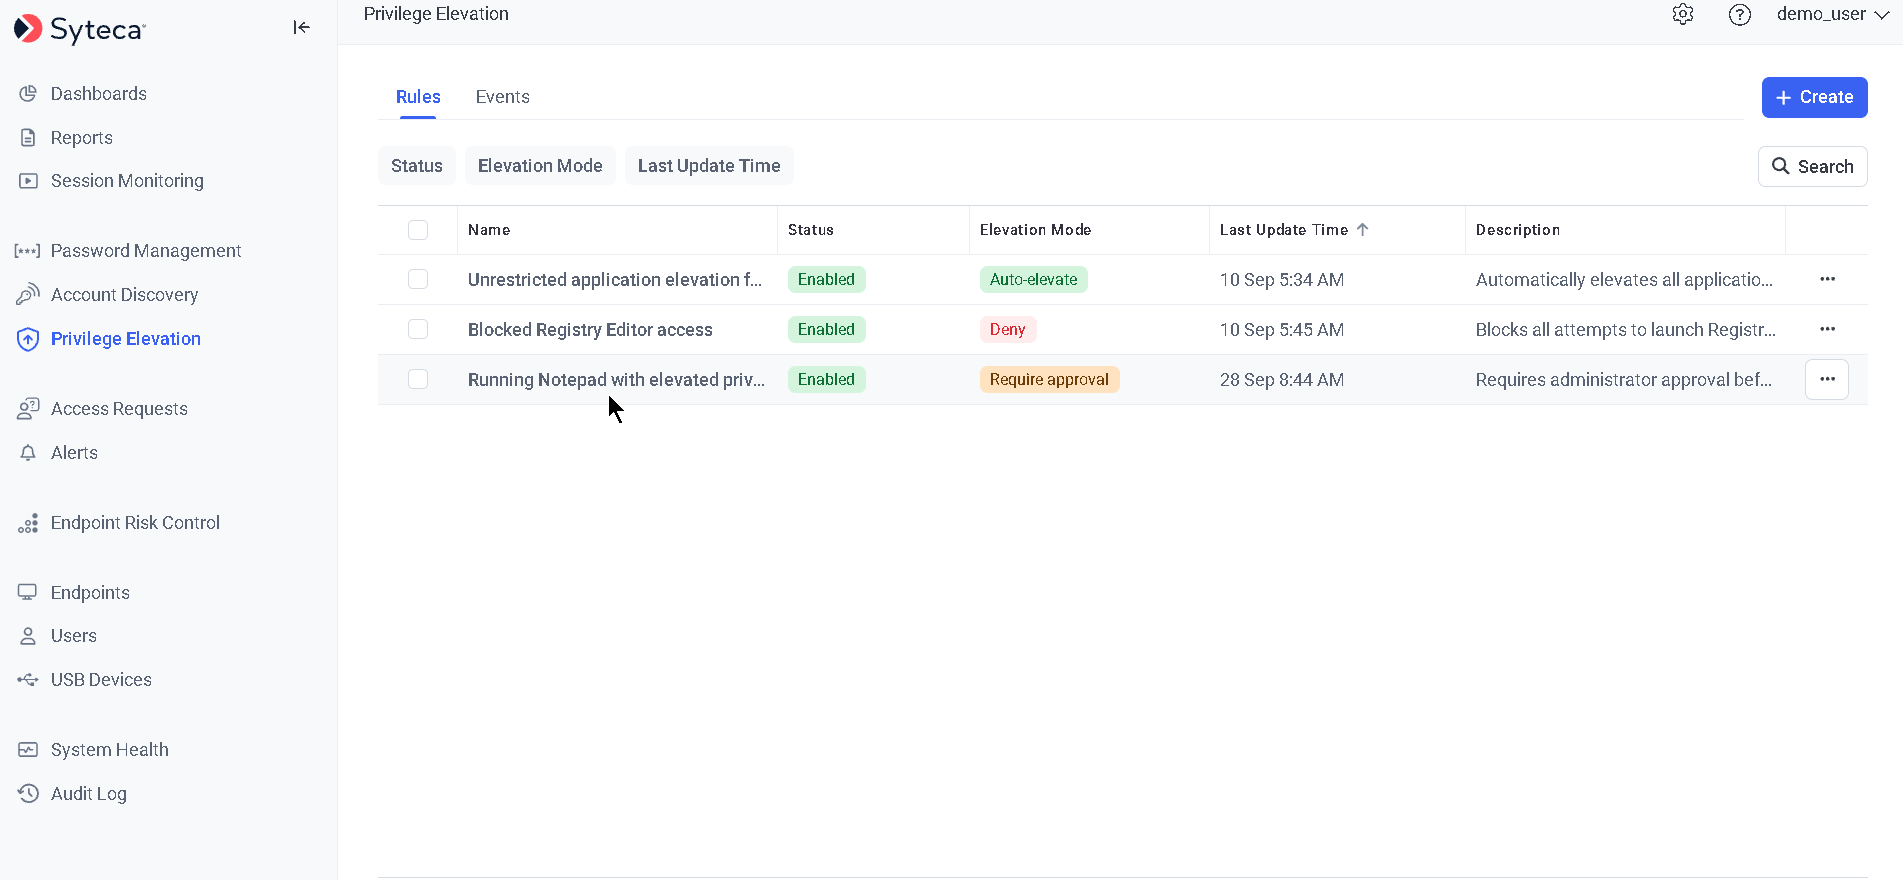
The Privilege Elevation Rules tab.
The rules grid
Column
Shows
Name
The rule’s name.
Status
Enabled or Disabled.
Elevation Mode
Auto-elevate, Require approval, or Deny.
Last Update Time
When the rule was last modified.
Description
Free-text notes on the rule.
Click the ⋮ menu next to a rule for Edit, Enable/Disable, or Delete.Filters: Status (multi-select), Elevation Mode (multi-select), Last Update Time (date range). Search matches Name and Description, full or partial text. Sort by Name or Last Update Time.
Bulk actions
Select multiple rules’ checkboxes to Enable, Disable, or Delete them together.
Bulk Enable/Disable shows a confirmation: “You are about to change the status of <N> selected rules. Are you sure you want to continue?”
Bulk Delete shows: “You are about to permanently delete <N> rules. Are you sure you want to continue?” — deletion is permanent.
Acting on a single rule through the ⋮ menu shows the same confirmations, naming the rule: “You are about to change the status of the <Rule Name> rule. Are you sure you want to continue?” and “You are about to permanently delete the <Rule Name> rule. Are you sure you want to continue?”
If you don’t want a rule to run but aren’t ready to delete it, you can disable it either from the grid’s ⋮ menu, via bulk action, or by clearing the Enabled toggle while editing the rule. A disabled rule stays in the system but is never evaluated.
Deleting a rule does not remove its history. Every elevation it produced stays on the Events tab.
Create a rule
Click Create on the Rules page to open the rule wizard: Details → Elevation Mode → Targeting Criteria → Assign Endpoints → Assigned Users → Summary. The Cancel button discards all changes and returns you to the Rules page.
The next tab stays unavailable until every required field on the tabs before it is complete. Once the rule has all its required settings, you can move freely between tabs.
1. Details
Field
Notes
Status toggle
Disabled by default, it can be enabled when the rule is ready to run.
Rule Name
Required, up to 200 characters, must be unique.
Description
Optional, up to 500 characters.
Notify if elevation failed
Optional checkbox, off by default.
Recipients
Required while Notify if elevation failed is checked. Select one or more users to email when an elevation attempt fails.
The failure notification names the rule, the assigned user and endpoint, the application, the reason, and the date and time. See when elevation fails for the conditions that trigger it.
The Details tab, with the notification settings at the bottom.
2. Elevation Mode
Choose the rule’s core action. Auto-elevate is selected by default.
Auto-elevate
Require approval
Deny
Launches the application with administrator rights immediately, with no prompt and no approval.Select credentials to use for privilege elevation is required. Choose one or more Secrets (Windows or Active Directory account types) to use as the elevation identity. Only Secrets you have at least PAM User permission on are available; click Add Secret in the drop-down to create one without leaving the wizard. See how the Secret is chosen below.Optionally, enable Auto-elevate during work hours to restrict automatic elevation to a schedule. The schedule fields become available, and mandatory, only while this toggle is on:
Field
Default
No date restriction / Allowed dates
No date restriction is selected by default. Selecting Allowed dates makes the date range mandatory and pre-fills it with 2 weeks starting from the rule’s creation date.
Allowed time
08:00 to 17:00.
Allowed days of the week
Monday to Friday. Clearing every day shows: “Select at least one day of the week.”
Action outside of work hours
Always deny, or Require approval.
Choosing Require approval here makes Users who can approve access mandatory. Choosing Always deny reveals a Show warning message to user checkbox, which works the same as on the Deny tab.
If a rule’s configured Allowed dates range expires, the rule doesn’t stop working. It falls back to whatever Action outside of work hours specifies (deny, or require approval).
The user submits a request, and an approver must sign in and approve it before the application launches with administrator rights.
Field
Notes
Require user’s comment
When on, the user must enter a reason before the request can be sent.
Users who can approve access
Required. Select the Management Tool users or user groups who can approve requests for this rule. An empty field shows: “This field is required.”
Select credentials to use for privilege elevation
Required. One or more Windows or Active Directory Secrets, as described under Auto-elevate.
Blocks the application launch automatically.Show warning message to user is optional. When enabled, the Message text field is required and holds up to 500 characters. An empty field shows: “This field is required.” The default message is: “According to company policy, your request for elevation to admin permissions was denied.”
The Elevation Mode tab, with Auto-elevate scheduling expanded.
Session recording during elevation sits in the Privilege Elevation Recording section and is off by default. It is available for Auto-elevate and Require approval; with Deny selected the section is shown as unavailable, because there is no elevated session to capture. When enabled, it records the screen, keyboard, and command input while a process is elevated, for audit and forensic purposes. See Events and monitoring for how this behaves depending on your license.
How the Secret is chosen
A rule can hold several Secrets. Which one is used is decided on the server, not on the endpoint:
1
The Client reports its state
On start, the Syteca Client sends the server whether the endpoint is domain-joined, along with its hostname and IP address.
2
The server picks one Secret
For a domain-joined endpoint, an Active Directory Secret from the rule is used. If none matches, the server matches the hostname or IP against the rule’s Windows Secrets. For an endpoint that isn’t domain-joined, the server matches hostname or IP against the Windows Secrets directly.
3
Only that Secret reaches the endpoint
The Client receives the single matched Secret. It never receives the rule’s full list of Secrets and never iterates through them locally.
If a rule holds only an Active Directory Secret and the endpoint isn’t domain-joined, elevation fails. See when elevation fails.
A Secret selected for privilege elevation can’t be deleted while it’s in use by a rule. See Delete a secret for the messages shown when deletion is blocked.
3. Targeting Criteria
Define what the rule matches against: manually, by uploading a file to extract its parameters, or both together. Manual and uploaded parameters combine with AND logic, and parameters of the same type combine with OR.
Manual entry
File upload
Choose a parameter type, a comparison operator, and a value. A new rule opens with File hash (SHA-256) and Equals already selected.
Parameter
Matches on
File hash (SHA-256)
The exact file hash.
Executable name(s)
The executable’s file name.
Path prefix
The folder path the executable runs from.
Digital signature
The signing publisher.
Command line
The full command line used to launch it.
The value field is required, holds up to 5000 characters, and accepts multiple values separated by semicolons. An empty field shows: “This field is required.”
Operator
Behavior
Value
Matches
Doesn’t match
Equals
Exact match.
notepad.exe
notepad.exe
notepad++.exe, calc.exe
Like
Value found as a substring.
notepad
notepad.exe, notepad-old.exe, backup-notepad.exe
calc.exe, editor.exe
Not equals
Does not exactly match.
notepad.exe
calc.exe, cmd.exe, explorer.exe
notepad.exe
Not like
Substring not found.
notepad
calc.exe, explorer.exe, cmd.exe
notepad.exe, notepad-old.exe, backup-notepad.exe
Matching is case-insensitive. A wildcard mask (* or *.exe) is supported for Like and Not like only.Click +Or to add another condition of the same logical group, or +And to add a condition that must also be true. Conditions of the same parameter type combine with OR; different parameter types combine with AND. The X button appears once a rule holds two or more conditions, and removes the one next to it.
In SaaS environments, file upload isn’t available. Use the Offline Parameters Extractor instead, a standalone utility that extracts the same four parameters from a .exe or .msi file entirely offline, so you can copy the values into your rule manually.Download the Offline Parameters Extractor and see Extract parameters offline below.
Upload a .exe or .msi file (up to 200 MB) and let Syteca extract its parameters automatically.
1
Upload the file
Drag and drop, or click to choose a file.
Invalid extension or oversized files show: “Upload failed. Please try again or choose another file.” Click Try again to reset the upload area and pick a different file.
2
Select the parameters to add
Once uploaded, the Extracted Application Parameters pop-up shows the extracted File hash (SHA-256), Executable name(s), Path prefix, and Digital signature, all unchecked. Select one or more checkboxes, then click Add. The Add button stays disabled until at least one is selected.
A parameter the system couldn’t extract shows Empty and can’t be selected. The uploaded file is deleted immediately after extraction and is not stored in any temporary or permanent location. It is never executed.
3
Add more files if needed
Click Add another file to repeat the process. If a newly extracted parameter matches one already in the rule (manually entered or from another file), it’s grouped with OR logic; otherwise it’s added with AND logic. The X next to an uploaded file name removes the file and every parameter it contributed.
The Extracted Application Parameters pop-up after uploading a file.
Once a rule holds five conditions, the tab shows a reminder: “Use simple rules to reduce rule evaluation time.”
Extract parameters offline
For SaaS customers, or anyone who prefers not to upload files to the Management Tool, the Offline Parameters Extractor is a small, standalone Windows utility you run locally.
The tool displays File hash (SHA-256), Executable name(s), Path prefix, and Digital signature, each with its own Copy button. A field that couldn’t be extracted shows Empty.
4
Paste into your rule
Paste the copied values into the corresponding manual-entry fields on the Targeting Criteria tab.
The tool never uploads or executes the file. It only reads it locally to extract metadata, and isn’t included in the standard server installation package.
4. Assign Endpoints
Select at least one endpoint or endpoint group. If none is selected, the tab shows: “At least one Endpoint or Endpoint group must be selected.”
Section
Selects
Domain Computer groups
A domain (only domains added via an LDAP target), typed into a text box with matching domains suggested as you type, and an Organizational Unit or computer group within it. Multiple values can be selected in the OU / Computers field. Supports * as a wildcard for any domain or local computer.
Endpoints
Individual endpoints where the Syteca Client is installed, or Select All.
Endpoint groups
Existing endpoint groups, or Select All.
Domain Computer groups combines with Endpoints and Endpoint groups using AND logic, so if you specify a domain group you must also select at least one endpoint or endpoint group. The Domain Computer group field on its own is not mandatory. Endpoints and Endpoint groups combine with each other using OR logic. The PAM Client group can’t be selected here.
Each added item appears with an X to remove it individually. Clear All appears once a section holds at least one item and removes everything in that section at once.
5. Assigned Users
Choose whether the rule applies to everyone, or to specific users. All is selected by default.
Option
Behavior
All
Applies to every user on the assigned endpoints.
Selected
Applies only to the users and user groups in the Users and User Groups grid. Leaving the grid empty shows: “No users or user groups selected. Add at least one user or user group to continue.”
Add entries to the grid with Add, then fill both columns:
Column
Accepts
Domain / Computer
A domain added through an LDAP target, or an endpoint where the Client is installed. Domains are listed first, endpoints below them. * is supported as a wildcard.
User / User group
Free text with autocomplete. * is supported as part of the value, for example *\Administrator.
Both columns are mandatory. An empty column shows “This field is required.” under the field, and the entry isn’t saved.Use the tick icon to save a row, the pencil icon to edit it, and the X icon to remove it. Remove All appears once the grid holds at least one entry.
Autocomplete queries Active Directory only when a Domain is selected, and returns at most 20 suggestions plus the exact text you typed. Selecting a Computer returns only the typed value, with no directory lookup. Selecting * searches across every available domain.
Exceptions are configured the same way, in their own grid, and always override the main selection. A user listed as an exception is excluded from the rule even if they would otherwise match.
The Exceptions grid is available with both All and Selected, and may be left empty. To apply a rule to everyone except a few people, choose All and list those people as exceptions. Choosing Selected and filling in only the Exceptions grid is not enough: the Users and User Groups grid still needs at least one entry.
6. Summary
Review every section before saving: Elevation Mode, Targeting Criteria, Assigned Endpoints, Assigned Users (with exceptions). Each section has its own Edit link, which jumps to the matching tab. An Impact preview shows the total number of endpoints the rule will affect.Where a section holds more than three values, only the first three are listed, followed by a +N more indicator. Clicking it reveals the rest.
If a required setting is missing (for example, Require approval selected with no approver defined), the Summary tab highlights it in a red error block so you can fix it before saving.
Click Save to activate the rule and return to the Rules page, where it now appears in the grid.
Edit a rule
Opening an existing rule for editing starts on the Summary tab, where you can jump to any section via the left navigation or that section’s Edit link. A tab opened through Edit behaves exactly as it does when you navigate to it manually.Changes are saved as you move between tabs, whether you use the tab navigation or the Next and Back buttons, and Save commits them and closes edit mode. Cancel discards changes made in that session and returns you to the Rules page. Mandatory fields left empty block saving and are highlighted.
How rules are matched
When a user runs something that triggers elevation, Syteca evaluates every enabled rule and works out which ones apply to the current context. A rule is matched only if all of the following hold:
The rule is enabled.
Its endpoint and user targeting covers the endpoint and the user.
Its targeting criteria match the application, whether entered manually or extracted from a file.
Its schedule constraints, if configured, are satisfied.
How conflicting rules resolve
If more than one enabled rule matches the same elevation attempt, Syteca doesn’t pick a rule arbitrarily. It applies the most restrictive matching decision, in this order:
Deny (most restrictive)
Require approval
Auto-elevate (least restrictive)
In other words: if even one matched rule says Deny, the result is Deny, regardless of what any other matched rule allows. If none say Deny but at least one says Require approval, the result is Require approval. Only if every matched rule says Auto-elevate does the attempt actually auto-elevate.
Rule A
Rule B
Result
Auto-elevate for notepad.exe
Deny for notepad.exe
Deny
Auto-elevate for mmc.exe
Require approval for mmc.exe
Require approval
Auto-elevate for cmd.exe
Auto-elevate for cmd.exe, different targeting
Auto-elevate
What happens when the Client starts enforcing a rule
1
No changes until the first rule is saved
After installing the Syteca Client, nothing changes on the endpoint until you save an enabled Privilege Elevation rule targeting it.
2
UAC is intercepted, not removed
Once a rule is active, the Syteca Client enforces Windows UAC settings so that elevation always triggers a prompt, making silent unmanaged elevation impossible, and intercepts that prompt before it completes to evaluate your rules against it.
3
Group membership is untouched
Privilege Elevation does not remove any user from the local Administrators group. It governs how elevation happens, not who’s technically capable of it.
Upgrading to a version with Privilege Elevation adds the new page and rules to the Management Tool but changes nothing by default. The native Windows UAC continues to work exactly as before until you create and enable your first rule.
Windows UAC policies that Privilege Elevation changes
To guarantee that every elevation attempt produces a prompt it can intercept, the Syteca Client sets four Windows UAC security policies on the endpoint:
Policy
Value Syteca sets
User Account Control: Run all administrators in Admin Approval Mode
Enabled
User Account Control: Behavior of the elevation prompt for administrators in Admin Approval Mode
Prompt for credentials on the secure desktop
User Account Control: Behavior of the elevation prompt for standard users
Prompt for credentials on the secure desktop
User Account Control: Admin Approval Mode for the Built-in Administrator account
Enabled
These policies live under Security Settings → Local Policies → Security Options in Local Security Policy or Group Policy.
A change to “Run all administrators in Admin Approval Mode” takes effect only after the endpoint restarts. Windows enables this policy by default, so endpoints where it has never been changed need no action. On endpoints where it has been disabled, Syteca sets it back to Enabled, and that endpoint must be rebooted before Privilege Elevation rules are enforced on it.
Review these four settings on your target endpoints before you deploy Privilege Elevation. If your organization has changed any of them away from the Windows defaults, include a reboot window in your rollout plan so the rules take effect when you expect them to.
Multi-tenant and high availability
In multi-tenant mode, the Privilege Elevation page is added to every tenant, and rule evaluation works the same way for a non-default tenant as for the default one.
Related
Overview
What Privilege Elevation does and how it’s licensed.
Events and monitoring
Every elevation decision, logged and searchable.
End-user experience
What a user sees when a rule applies to them.
Add a secret
Create the Secret a Require approval or Auto-elevate rule uses.
{"docsConfig":{"theme":"mint","$schema":"https://mintlify.com/docs.json","name":"Syteca","description":"Syteca documentation - User Activity Monitoring and Privileged Access Management in a single platform.","colors":{"primary":"#2563EB","light":"#5B8DEF","dark":"#1D4ED8"},"logo":{"light":"https://mintcdn.com/syteca/ZVta4JfIcSnC47NX/logo/syteca-light.svg?fit=max\u0026auto=format\u0026n=ZVta4JfIcSnC47NX\u0026q=85\u0026s=154a18f69aa4aefa55de0de7669934c7","dark":"https://mintcdn.com/syteca/ZVta4JfIcSnC47NX/logo/syteca-dark.svg?fit=max\u0026auto=format\u0026n=ZVta4JfIcSnC47NX\u0026q=85\u0026s=07170d0c543f4264cca523f1b74b912e","href":"https://www.syteca.com/docs"},"favicon":"https://mintcdn.com/syteca/0FlD-vkHsBA1azVX/favicon.ico?fit=max\u0026auto=format\u0026n=0FlD-vkHsBA1azVX\u0026q=85\u0026s=6c6a5b9e7da5f386c9d031d55704987a","appearance":{"default":"system","strict":false},"background":{"decoration":"grid","color":{"light":"#FFFFFF","dark":"#0B0D12"}},"navbar":{"links":[{"href":"https://www.syteca.com/docs/release-notes/overview","label":"Changelog"},{"href":"https://www.syteca.com/docs/api/acb/api-reference","label":"API Reference"},{"href":"https://www.syteca.com/en/support/contact-support","label":"Support"}],"primary":{"type":"button","label":"Book a Demo","href":"https://www.syteca.com/en/book-a-demo"}},"footer":{"socials":{"youtube":"https://www.youtube.com/@syteca","linkedin":"https://www.linkedin.com/company/syteca.com"},"links":[{"header":"Product","items":[{"label":"Overview","href":"https://www.syteca.com/docs"},{"label":"Releases","href":"https://www.syteca.com/docs/release-notes/overview"},{"label":"Pricing","href":"https://syteca.com/pricing"}]},{"header":"Company","items":[{"label":"About","href":"https://www.syteca.com/en/company/about-us"}]},{"header":"Legal","items":[{"label":"Privacy","href":"https://syteca.com/privacy"},{"label":"Terms","href":"https://www.syteca.com/en/terms-of-use"}]}]},"search":{"prompt":"Syteca Documentation"},"seo":{"metatags":{"og:image":"https://www.syteca.com/og-default.png","og:site_name":"Syteca Docs","canonical":"https://www.syteca.com/docs"}},"fonts":{"heading":{"family":"Inter","weight":700},"body":{"family":"Inter","weight":400}},"icons":{"library":"lucide"},"styling":{"eyebrows":"section","codeblocks":"system","latex":false},"integrations":{"ga4":{"measurementId":"G-3SYH6XSJXQ"}},"errors":{"404":{"redirect":false}},"navigation":{"pages":[]}},"deployment":{"deploymentMetadataValue":{"subdomain":"syteca","hasAudioNarration":false,"actualSubdomain":"syteca","customDomains":["syteca.com"],"gitSource":{"type":"github","owner":"syteca","repo":"syteca-docs-poc","deployBranch":"main","contentDirectory":"","isPrivate":true,"mountPath":"","label":""},"feedback":{"thumbs":false},"entitlements":{"AI_CHAT":{"status":"DISABLED"}},"buildId":"6afd11321c0e198c9c436271","clientVersion":"0.0.4205","searchFilterCounts":[{"language":"default","tag":"Administration","count":97},{"language":"default","tag":"API \u0026 Integrations","count":84},{"language":"default","tag":"Application Credentials Broker","count":53},{"language":"default","tag":"Session Monitoring","count":43},{"language":"default","tag":"Endpoint Risk Control","count":31},{"language":"default","tag":"Endpoints","count":30},{"language":"default","tag":"Privileged Access Management","count":26},{"language":"default","tag":"Release Notes","count":24},{"language":"default","tag":"Get Started","count":18},{"language":"default","tag":"Syteca changelog","count":18}]},"assistantConfig":{"enableAskAiButton":false,"enableStarterQuestions":false,"enableContextualStarterQuestions":false,"enableAskAiSearchBar":true},"basePath":"/docs","hasChatPermissions":false,"hasWebMcpPermissions":false,"toggles":[{"name":"kill-isr","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"custom-rbac-roles","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-mintlify-slack","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-integrations-settings","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"rbac-expansion","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-pr-grouping","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"custom-prefix","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"analytics-v7","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"user-flows-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"no-publish-flow","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-onboarding","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving-live","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"stripTemperatureMiddleware","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"support-platform-pylon-zendesk","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"instant-rollback","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications-server","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-fable","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fixed-ai-action-pricing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automation-resolve-merge-conflict","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"scoped-publishing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"mintql","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"page-level-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"editor-version-history-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"billing-page-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"full-page-search","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workspace-projects","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"assistant-v5","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fork-pr-previews","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"revalidation-jwt","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-sso-scim","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"hobby-abuse-scan","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"dashboard-inbox","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-signup","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"turbopuffer-dual-write","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-enabled","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"approve-review-flow","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"editor-metadata","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"sso-setup-deadline-banner","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"turbopuffer-serve","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"live-agents","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"starter-pricing","enabled":true,"variant":{"name":"treatment","enabled":true,"payload":{"type":"string","value":"treatment"},"feature_enabled":true},"impressionData":false},{"name":"llms-txt-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"wildcard-email-auth","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false}],"googleFontsInlined":false},"customCss":[{"filePath":"style.css","content":":root{--syteca-brand: #2563EB;--syteca-brand-strong: #1D4ED8;--syteca-brand-soft: #EFF6FF;--syteca-accent-green: #16A34A;--syteca-accent-amber: #D97706;--syteca-accent-violet: #7C3AED;--syteca-accent-rose: #DB2777;--syteca-accent-cyan: #0891B2;--syteca-accent-teal: #0D9488}html.dark{--syteca-brand: #5B8DEF;--syteca-brand-strong: #7AA1F3;--syteca-brand-soft: #14213D}.prose h1{letter-spacing:-0.025em}.prose h2{letter-spacing:-0.015em}a[class*=\"rounded-\"][class*=\"border\"]:hover{transform:translateY(-1px);transition:transform 150ms ease, box-shadow 150ms ease, border-color 150ms ease}.prose pre,.prose code{font-family:\"JetBrains Mono\", \"SF Mono\", \"Menlo\", \"Consolas\", monospace}.prose table thead th{border-bottom:2px solid var(--syteca-brand);font-weight:600}.prose table tbody td{padding-top:0.55rem;padding-bottom:0.55rem}figure figcaption{font-size:13px;color:rgb(113 113 122 / 1);margin-top:0.6rem}nav[aria-label=\"Sidebar\"] a{padding-top:0.3rem;padding-bottom:0.3rem;font-size:13.5px}.demo-bar{display:none}"}],"page":{"pagePath":"pam/privilege-elevation/rules","slug":"/pam/privilege-elevation/rules","pageMetadata":{"title":"Creating and Managing Privilege Elevation Rules","sidebarTitle":"Rules","description":"Build Privilege Elevation rules that decide when a Windows application should Auto-elevate, require approval, or be denied. It includes targeting criteria, endpoints, users, and how conflicting rules resolve.","icon":"list-checks","keywords":["syteca privilege elevation rules","auto-elevate require approval deny","pedm targeting criteria","offline parameters extractor","syteca uac rule priority","uac admin approval mode","privilege elevation uac policy reboot"],"href":"/pam/privilege-elevation/rules"},"description":{"compiledSource":"\"use strict\";\nconst {jsx: _jsx} = arguments[0];\nconst {useMDXComponents: _provideComponents} = arguments[0];\nfunction _createMdxContent(props) {\n const _components = {\n p: \"p\",\n ..._provideComponents(),\n ...props.components\n };\n return _jsx(_components.p, {\n children: \"Build Privilege Elevation rules that decide when a Windows application should Auto-elevate, require approval, or be denied. It includes targeting criteria, endpoints, users, and how conflicting rules resolve.\"\n });\n}\nfunction MDXContent(props = {}) {\n const {wrapper: MDXLayout} = {\n ..._provideComponents(),\n ...props.components\n };\n return MDXLayout ? _jsx(MDXLayout, {\n ...props,\n children: _jsx(_createMdxContent, {\n ...props\n })\n }) : _createMdxContent(props);\n}\nreturn {\n default: MDXContent\n};\n","frontmatter":{},"scope":{}},"pageType":"default","mdx":{"mdxSource":{"compiledSource":"\"use strict\";const{Fragment:_Fragment,jsx:_jsx,jsxs:_jsxs}=arguments[0];const{useMDXComponents:_provideComponents}=arguments[0];function _createMdxContent(props){const _components={a:`a`,code:`code`,em:`em`,li:`li`,ol:`ol`,p:`p`,strong:`strong`,tbody:`tbody`,td:`td`,th:`th`,thead:`thead`,tr:`tr`,ul:`ul`,..._provideComponents(),...props.components},{Card,CardGroup,Frame,Heading,Note,OptimizedImage,Step,Steps,Tab,Table,Tabs,Tip,Warning}=_components;if(!Card)_missingMdxReference(`Card`,true);if(!CardGroup)_missingMdxReference(`CardGroup`,true);if(!Frame)_missingMdxReference(`Frame`,true);if(!Heading)_missingMdxReference(`Heading`,true);if(!Note)_missingMdxReference(`Note`,true);if(!OptimizedImage)_missingMdxReference(`OptimizedImage`,true);if(!Step)_missingMdxReference(`Step`,true);if(!Steps)_missingMdxReference(`Steps`,true);if(!Tab)_missingMdxReference(`Tab`,true);if(!Table)_missingMdxReference(`Table`,true);if(!Tabs)_missingMdxReference(`Tabs`,true);if(!Tip)_missingMdxReference(`Tip`,true);if(!Warning)_missingMdxReference(`Warning`,true);return _jsxs(_Fragment,{children:[_jsxs(_components.p,{children:[`A `,_jsx(_components.strong,{children:`Privilege Elevation rule`}),` defines what triggers it (which application, on which endpoints, for which users) and what happens when it does: `,_jsx(_components.strong,{children:`Auto-elevate`}),`, `,_jsx(_components.strong,{children:`Require approval`}),`, or `,_jsx(_components.strong,{children:`Deny`}),`.`]}),`\n`,_jsx(Heading,{level:`2`,id:`the-rules-page`,children:`The Rules page`}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`Open Privilege Elevation`,children:_jsxs(_components.p,{children:[`Log in as a user with the `,_jsx(_components.strong,{children:`Privilege Elevation`}),` administrative permission. In the left navigation click `,_jsx(_components.strong,{children:`Privilege Elevation`}),`.`]})}),_jsx(Step,{title:`Select the Rules tab`,children:_jsxs(_components.p,{children:[`The `,_jsx(_components.strong,{children:`Rules`}),` tab shows every configured rule in a grid. It is empty by default until you create one.`]})})]}),`\n`,_jsx(Note,{children:_jsxs(_components.p,{children:[`Any Management Tool user with the `,_jsx(_components.strong,{children:`Privilege Elevation`}),` administrative permission can create, edit, enable, disable, and delete `,_jsx(_components.strong,{children:`any`}),` rule, regardless of who created it. There are no per-rule permissions and no rule owner.`]})}),`\n`,_jsx(Frame,{caption:`The Privilege Elevation Rules tab.`,children:_jsx(OptimizedImage,{src:`https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rules-tab-overview.png?fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=4edd67d5c094bdc88d3f579677698562`,alt:`Privilege Elevation Rules tab with the rules grid`,\"data-og-width\":`1903`,width:`1903`,\"data-og-height\":`880`,height:`880`,\"data-path\":`images/pam/privilege-elevation/rules-tab-overview.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rules-tab-overview.png?w=280\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=383a2293020c9eb00a1c68d151e5c7bb 280w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rules-tab-overview.png?w=560\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=0333b0cd0a615e6ca4a779858a4d7f8a 560w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rules-tab-overview.png?w=840\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=018e69d7577df248c5ae7253da03b784 840w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rules-tab-overview.png?w=1100\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=9d5a942b47828b3331bac08e9a023ee8 1100w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rules-tab-overview.png?w=1650\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=cd7b407689e728e0ea59fd89879d89ff 1650w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rules-tab-overview.png?w=2500\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=befd8d0a7a8e6d928701ba4a434f60c0 2500w`})}),`\n`,_jsx(Heading,{level:`3`,id:`the-rules-grid`,children:`The rules grid`}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Column`}),_jsx(_components.th,{children:`Shows`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Name`})}),_jsx(_components.td,{children:`The rule’s name.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Status`})}),_jsxs(_components.td,{children:[_jsx(_components.strong,{children:`Enabled`}),` or `,_jsx(_components.strong,{children:`Disabled`}),`.`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Elevation Mode`})}),_jsxs(_components.td,{children:[_jsx(_components.strong,{children:`Auto-elevate`}),`, `,_jsx(_components.strong,{children:`Require approval`}),`, or `,_jsx(_components.strong,{children:`Deny`}),`.`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Last Update Time`})}),_jsx(_components.td,{children:`When the rule was last modified.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Description`})}),_jsx(_components.td,{children:`Free-text notes on the rule.`})]})]})]}),`\n`,_jsxs(_components.p,{children:[`Click the `,_jsx(_components.strong,{children:`⋮`}),` menu next to a rule for `,_jsx(_components.strong,{children:`Edit`}),`, `,_jsx(_components.strong,{children:`Enable/Disable`}),`, or `,_jsx(_components.strong,{children:`Delete`}),`.`]}),`\n`,_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Filters:`}),` Status (multi-select), Elevation Mode (multi-select), Last Update Time (date range). `,_jsx(_components.strong,{children:`Search`}),` matches Name and Description, full or partial text. `,_jsx(_components.strong,{children:`Sort`}),` by Name or Last Update Time.`]}),`\n`,_jsx(Heading,{level:`3`,id:`bulk-actions`,children:`Bulk actions`}),`\n`,_jsxs(_components.p,{children:[`Select multiple rules’ checkboxes to `,_jsx(_components.strong,{children:`Enable`}),`, `,_jsx(_components.strong,{children:`Disable`}),`, or `,_jsx(_components.strong,{children:`Delete`}),` them together.`]}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`Bulk `,_jsx(_components.strong,{children:`Enable/Disable`}),` shows a confirmation: `,_jsx(_components.em,{children:`“You are about to change the status of \u003cN> selected rules. Are you sure you want to continue?”`})]}),`\n`,_jsxs(_components.li,{children:[`Bulk `,_jsx(_components.strong,{children:`Delete`}),` shows: `,_jsx(_components.em,{children:`“You are about to permanently delete \u003cN> rules. Are you sure you want to continue?”`}),` — deletion is permanent.`]}),`\n`]}),`\n`,_jsxs(_components.p,{children:[`Acting on a single rule through the `,_jsx(_components.strong,{children:`⋮`}),` menu shows the same confirmations, naming the rule: `,_jsx(_components.em,{children:`“You are about to change the status of the \u003cRule Name> rule. Are you sure you want to continue?”`}),` and `,_jsx(_components.em,{children:`“You are about to permanently delete the \u003cRule Name> rule. Are you sure you want to continue?”`})]}),`\n`,_jsx(Tip,{children:_jsxs(_components.p,{children:[`If you don’t want a rule to run but aren’t ready to delete it, you can disable it either from the grid’s `,_jsx(_components.strong,{children:`⋮`}),` menu, via bulk action, or by clearing the `,_jsx(_components.strong,{children:`Enabled`}),` toggle while editing the rule. A disabled rule stays in the system but is never evaluated.`]})}),`\n`,_jsx(Note,{children:_jsxs(_components.p,{children:[`Deleting a rule does not remove its history. Every elevation it produced stays on the `,_jsx(_components.a,{href:`/pam/privilege-elevation/events`,children:`Events`}),` tab.`]})}),`\n`,_jsx(Heading,{level:`2`,id:`create-a-rule`,children:`Create a rule`}),`\n`,_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Create`}),` on the Rules page to open the rule wizard: `,_jsx(_components.strong,{children:`Details → Elevation Mode → Targeting Criteria → Assign Endpoints → Assigned Users → Summary`}),`. The `,_jsx(_components.strong,{children:`Cancel`}),` button discards all changes and returns you to the Rules page.`]}),`\n`,_jsx(Note,{children:_jsx(_components.p,{children:`The next tab stays unavailable until every required field on the tabs before it is complete. Once the rule has all its required settings, you can move freely between tabs.`})}),`\n`,_jsx(Heading,{level:`3`,id:`1-details`,children:`1. Details`}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Field`}),_jsx(_components.th,{children:`Notes`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsxs(_components.td,{children:[_jsx(_components.strong,{children:`Status`}),` toggle`]}),_jsx(_components.td,{children:`Disabled by default, it can be enabled when the rule is ready to run.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Rule Name`})}),_jsx(_components.td,{children:`Required, up to 200 characters, must be unique.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Description`})}),_jsx(_components.td,{children:`Optional, up to 500 characters.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Notify if elevation failed`})}),_jsx(_components.td,{children:`Optional checkbox, off by default.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Recipients`})}),_jsxs(_components.td,{children:[`Required while `,_jsx(_components.strong,{children:`Notify if elevation failed`}),` is checked. Select one or more users to email when an elevation attempt fails.`]})]})]})]}),`\n`,_jsxs(_components.p,{children:[`The failure notification names the rule, the assigned user and endpoint, the application, the reason, and the date and time. See `,_jsx(_components.a,{href:`/pam/privilege-elevation/end-user-experience#when-elevation-fails-outright`,children:`when elevation fails`}),` for the conditions that trigger it.`]}),`\n`,_jsx(Frame,{caption:`The Details tab, with the notification settings at the bottom.`,children:_jsx(OptimizedImage,{src:`https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-details-tab.png?fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=3cd5a119fb64628c8a86719cef6897c5`,alt:`Details tab of the Privilege Elevation rule wizard showing rule name, description, and failure notification settings`,\"data-og-width\":`1883`,width:`1883`,\"data-og-height\":`934`,height:`934`,\"data-path\":`images/pam/privilege-elevation/rule-details-tab.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-details-tab.png?w=280\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=67bd590da16b0d884530227013679b01 280w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-details-tab.png?w=560\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=896a0f22ed39ab46ee01d8cd31c61793 560w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-details-tab.png?w=840\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=afe2504cbe92a63187f6c3b9cf0a33ba 840w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-details-tab.png?w=1100\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=e8fbd69bd897ca94430af92ddccc0e43 1100w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-details-tab.png?w=1650\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=9e287e4db934cd00e04441ec1c0eeecd 1650w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-details-tab.png?w=2500\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=529c6ce8c242fc0f72641662c6966ebd 2500w`})}),`\n`,_jsx(Heading,{level:`3`,id:`2-elevation-mode`,children:`2. Elevation Mode`}),`\n`,_jsxs(_components.p,{children:[`Choose the rule’s core action. `,_jsx(_components.strong,{children:`Auto-elevate`}),` is selected by default.`]}),`\n`,_jsxs(Tabs,{children:[_jsxs(Tab,{title:`Auto-elevate`,id:`auto-elevate`,children:[_jsx(_components.p,{children:`Launches the application with administrator rights immediately, with no prompt and no approval.`}),_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Select credentials to use for privilege elevation`}),` is required. Choose one or more Secrets (Windows or Active Directory account types) to use as the elevation identity. Only Secrets you have at least `,_jsx(_components.strong,{children:`PAM User`}),` permission on are available; click `,_jsx(_components.strong,{children:`Add Secret`}),` in the drop-down to create one without leaving the wizard. See `,_jsx(_components.a,{href:`#how-the-secret-is-chosen`,children:`how the Secret is chosen`}),` below.`]}),_jsxs(_components.p,{children:[`Optionally, enable `,_jsx(_components.strong,{children:`Auto-elevate during work hours`}),` to restrict automatic elevation to a schedule. The schedule fields become available, and mandatory, only while this toggle is on:`]}),_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Field`}),_jsx(_components.th,{children:`Default`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsxs(_components.td,{children:[_jsx(_components.strong,{children:`No date restriction`}),` / `,_jsx(_components.strong,{children:`Allowed dates`})]}),_jsxs(_components.td,{children:[_jsx(_components.strong,{children:`No date restriction`}),` is selected by default. Selecting `,_jsx(_components.strong,{children:`Allowed dates`}),` makes the date range mandatory and pre-fills it with 2 weeks starting from the rule’s creation date.`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Allowed time`})}),_jsx(_components.td,{\"data-numeric\":`true`,children:`08:00 to 17:00.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Allowed days of the week`})}),_jsxs(_components.td,{children:[`Monday to Friday. Clearing every day shows: `,_jsx(_components.em,{children:`“Select at least one day of the week.”`})]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Action outside of work hours`})}),_jsxs(_components.td,{children:[_jsx(_components.strong,{children:`Always deny`}),`, or `,_jsx(_components.strong,{children:`Require approval`}),`.`]})]})]})]}),_jsxs(_components.p,{children:[`Choosing `,_jsx(_components.strong,{children:`Require approval`}),` here makes `,_jsx(_components.strong,{children:`Users who can approve access`}),` mandatory. Choosing `,_jsx(_components.strong,{children:`Always deny`}),` reveals a `,_jsx(_components.strong,{children:`Show warning message to user`}),` checkbox, which works the same as on the Deny tab.`]}),_jsx(Note,{children:_jsxs(_components.p,{children:[`If a rule’s configured `,_jsx(_components.strong,{children:`Allowed dates`}),` range expires, the rule doesn’t stop working. It falls back to whatever `,_jsx(_components.strong,{children:`Action outside of work hours`}),` specifies (deny, or require approval).`]})})]}),_jsxs(Tab,{title:`Require approval`,id:`require-approval`,children:[_jsx(_components.p,{children:`The user submits a request, and an approver must sign in and approve it before the application launches with administrator rights.`}),_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Field`}),_jsx(_components.th,{children:`Notes`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Require user’s comment`})}),_jsx(_components.td,{children:`When on, the user must enter a reason before the request can be sent.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Users who can approve access`})}),_jsxs(_components.td,{children:[`Required. Select the Management Tool users or user groups who can approve requests for this rule. An empty field shows: `,_jsx(_components.em,{children:`“This field is required.”`})]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Select credentials to use for privilege elevation`})}),_jsx(_components.td,{children:`Required. One or more Windows or Active Directory Secrets, as described under Auto-elevate.`})]})]})]})]}),_jsxs(Tab,{title:`Deny`,id:`deny`,children:[_jsx(_components.p,{children:`Blocks the application launch automatically.`}),_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Show warning message to user`}),` is optional. When enabled, the `,_jsx(_components.strong,{children:`Message text`}),` field is required and holds up to 500 characters. An empty field shows: `,_jsx(_components.em,{children:`“This field is required.”`}),` The default message is: `,_jsx(_components.em,{children:`“According to company policy, your request for elevation to admin permissions was denied.”`})]})]})]}),`\n`,_jsx(Frame,{caption:`The Elevation Mode tab, with Auto-elevate scheduling expanded.`,children:_jsx(OptimizedImage,{src:`https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-elevation-mode-tab.png?fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=59c5cb5e74bcfcb1167d63b5651cd3c1`,alt:`Elevation Mode tab showing Auto-elevate, Require approval, and Deny options`,\"data-og-width\":`1894`,width:`1894`,\"data-og-height\":`961`,height:`961`,\"data-path\":`images/pam/privilege-elevation/rule-elevation-mode-tab.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-elevation-mode-tab.png?w=280\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=831dfab704dc75daea7b12abeba7dcec 280w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-elevation-mode-tab.png?w=560\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=5cba13eb5b81dc9ac7e4e6143194ef99 560w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-elevation-mode-tab.png?w=840\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=3d818793a35f3e99d28b4a03c3edcb0a 840w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-elevation-mode-tab.png?w=1100\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=842f2b2efbb41e4eb6518d1fc83bc2c7 1100w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-elevation-mode-tab.png?w=1650\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=07ed357f77ea38c7ea2fc1e9354ff27a 1650w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-elevation-mode-tab.png?w=2500\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=d3eed60c15876d4191060c5e7b36a9f4 2500w`})}),`\n`,_jsx(Note,{children:_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Session recording during elevation`}),` sits in the `,_jsx(_components.strong,{children:`Privilege Elevation Recording`}),` section and is off by default. It is available for `,_jsx(_components.strong,{children:`Auto-elevate`}),` and `,_jsx(_components.strong,{children:`Require approval`}),`; with `,_jsx(_components.strong,{children:`Deny`}),` selected the section is shown as unavailable, because there is no elevated session to capture. When enabled, it records the screen, keyboard, and command input while a process is elevated, for audit and forensic purposes. See `,_jsx(_components.a,{href:`/pam/privilege-elevation/events#session-recording-during-elevation`,children:`Events and monitoring`}),` for how this behaves depending on your license.`]})}),`\n`,_jsx(Heading,{level:`4`,id:`how-the-secret-is-chosen`,children:`How the Secret is chosen`}),`\n`,_jsx(_components.p,{children:`A rule can hold several Secrets. Which one is used is decided on the server, not on the endpoint:`}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`The Client reports its state`,children:_jsx(_components.p,{children:`On start, the Syteca Client sends the server whether the endpoint is domain-joined, along with its hostname and IP address.`})}),_jsx(Step,{title:`The server picks one Secret`,children:_jsx(_components.p,{children:`For a domain-joined endpoint, an Active Directory Secret from the rule is used. If none matches, the server matches the hostname or IP against the rule’s Windows Secrets. For an endpoint that isn’t domain-joined, the server matches hostname or IP against the Windows Secrets directly.`})}),_jsx(Step,{title:`Only that Secret reaches the endpoint`,children:_jsx(_components.p,{children:`The Client receives the single matched Secret. It never receives the rule’s full list of Secrets and never iterates through them locally.`})})]}),`\n`,_jsx(Warning,{children:_jsxs(_components.p,{children:[`If a rule holds only an Active Directory Secret and the endpoint isn’t domain-joined, elevation fails. See `,_jsx(_components.a,{href:`/pam/privilege-elevation/end-user-experience#when-elevation-fails-outright`,children:`when elevation fails`}),`.`]})}),`\n`,_jsx(Warning,{children:_jsxs(_components.p,{children:[`A Secret selected for privilege elevation can’t be deleted while it’s in use by a rule. See `,_jsx(_components.a,{href:`/pam/secrets/delete-secret#when-a-secret-cannot-be-deleted`,children:`Delete a secret`}),` for the messages shown when deletion is blocked.`]})}),`\n`,_jsx(Heading,{level:`3`,id:`3-targeting-criteria`,children:`3. Targeting Criteria`}),`\n`,_jsx(_components.p,{children:`Define what the rule matches against: manually, by uploading a file to extract its parameters, or both together. Manual and uploaded parameters combine with AND logic, and parameters of the same type combine with OR.`}),`\n`,_jsxs(Tabs,{children:[_jsxs(Tab,{title:`Manual entry`,id:`manual-entry`,children:[_jsxs(_components.p,{children:[`Choose a parameter type, a comparison operator, and a value. A new rule opens with `,_jsx(_components.strong,{children:`File hash (SHA-256)`}),` and `,_jsx(_components.strong,{children:`Equals`}),` already selected.`]}),_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Parameter`}),_jsx(_components.th,{children:`Matches on`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`File hash (SHA-256)`}),_jsx(_components.td,{children:`The exact file hash.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`Executable name(s)`}),_jsx(_components.td,{children:`The executable’s file name.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`Path prefix`}),_jsx(_components.td,{children:`The folder path the executable runs from.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`Digital signature`}),_jsx(_components.td,{children:`The signing publisher.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`Command line`}),_jsx(_components.td,{children:`The full command line used to launch it.`})]})]})]}),_jsxs(_components.p,{children:[`The `,_jsx(_components.strong,{children:`value`}),` field is required, holds up to 5000 characters, and accepts multiple values separated by semicolons. An empty field shows: `,_jsx(_components.em,{children:`“This field is required.”`})]}),_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Operator`}),_jsx(_components.th,{children:`Behavior`}),_jsx(_components.th,{children:`Value`}),_jsx(_components.th,{children:`Matches`}),_jsx(_components.th,{children:`Doesn’t match`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Equals`})}),_jsx(_components.td,{children:`Exact match.`}),_jsx(_components.td,{children:_jsx(_components.code,{children:`notepad.exe`})}),_jsx(_components.td,{children:_jsx(_components.code,{children:`notepad.exe`})}),_jsxs(_components.td,{children:[_jsx(_components.code,{children:`notepad++.exe`}),`, `,_jsx(_components.code,{children:`calc.exe`})]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Like`})}),_jsx(_components.td,{children:`Value found as a substring.`}),_jsx(_components.td,{children:_jsx(_components.code,{children:`notepad`})}),_jsxs(_components.td,{children:[_jsx(_components.code,{children:`notepad.exe`}),`, `,_jsx(_components.code,{children:`notepad-old.exe`}),`, `,_jsx(_components.code,{children:`backup-notepad.exe`})]}),_jsxs(_components.td,{children:[_jsx(_components.code,{children:`calc.exe`}),`, `,_jsx(_components.code,{children:`editor.exe`})]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Not equals`})}),_jsx(_components.td,{children:`Does not exactly match.`}),_jsx(_components.td,{children:_jsx(_components.code,{children:`notepad.exe`})}),_jsxs(_components.td,{children:[_jsx(_components.code,{children:`calc.exe`}),`, `,_jsx(_components.code,{children:`cmd.exe`}),`, `,_jsx(_components.code,{children:`explorer.exe`})]}),_jsx(_components.td,{children:_jsx(_components.code,{children:`notepad.exe`})})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Not like`})}),_jsx(_components.td,{children:`Substring not found.`}),_jsx(_components.td,{children:_jsx(_components.code,{children:`notepad`})}),_jsxs(_components.td,{children:[_jsx(_components.code,{children:`calc.exe`}),`, `,_jsx(_components.code,{children:`explorer.exe`}),`, `,_jsx(_components.code,{children:`cmd.exe`})]}),_jsxs(_components.td,{children:[_jsx(_components.code,{children:`notepad.exe`}),`, `,_jsx(_components.code,{children:`notepad-old.exe`}),`, `,_jsx(_components.code,{children:`backup-notepad.exe`})]})]})]})]}),_jsxs(_components.p,{children:[`Matching is case-insensitive. A wildcard mask (`,_jsx(_components.code,{children:`*`}),` or `,_jsx(_components.code,{children:`*.exe`}),`) is supported for `,_jsx(_components.strong,{children:`Like`}),` and `,_jsx(_components.strong,{children:`Not like`}),` only.`]}),_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`+Or`}),` to add another condition of the same logical group, or `,_jsx(_components.strong,{children:`+And`}),` to add a condition that must also be true. Conditions of the same parameter type combine with OR; different parameter types combine with AND. The `,_jsx(_components.strong,{children:`X`}),` button appears once a rule holds two or more conditions, and removes the one next to it.`]})]}),_jsxs(Tab,{title:`File upload`,id:`file-upload`,children:[_jsx(Warning,{children:_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`In SaaS environments, file upload isn’t available.`}),` Use the `,_jsx(_components.strong,{children:`Offline Parameters Extractor`}),` instead, a standalone utility that extracts the same four parameters from a `,_jsx(_components.code,{children:`.exe`}),` or `,_jsx(_components.code,{children:`.msi`}),` file entirely offline, so you can copy the values into your rule manually.`,_jsx(_components.a,{href:`https://download.syteca.com/Offline_Parameters_Extractor.exe`,children:`Download the Offline Parameters Extractor`}),` and see `,_jsx(_components.a,{href:`#extract-parameters-offline`,children:`Extract parameters offline`}),` below.`]})}),_jsxs(_components.p,{children:[`Upload a `,_jsx(_components.code,{children:`.exe`}),` or `,_jsx(_components.code,{children:`.msi`}),` file (up to 200 MB) and let Syteca extract its parameters automatically.`]}),_jsxs(Steps,{children:[_jsxs(Step,{title:`Upload the file`,children:[_jsx(_components.p,{children:`Drag and drop, or click to choose a file.`}),_jsx(Note,{children:_jsxs(_components.p,{children:[`Invalid extension or oversized files show: `,_jsx(_components.em,{children:`“Upload failed. Please try again or choose another file.”`}),` Click `,_jsx(_components.strong,{children:`Try again`}),` to reset the upload area and pick a different file.`]})})]}),_jsxs(Step,{title:`Select the parameters to add`,children:[_jsxs(_components.p,{children:[`Once uploaded, the `,_jsx(_components.strong,{children:`Extracted Application Parameters`}),` pop-up shows the extracted `,_jsx(_components.strong,{children:`File hash (SHA-256)`}),`, `,_jsx(_components.strong,{children:`Executable name(s)`}),`, `,_jsx(_components.strong,{children:`Path prefix`}),`, and `,_jsx(_components.strong,{children:`Digital signature`}),`, all unchecked. Select one or more checkboxes, then click `,_jsx(_components.strong,{children:`Add`}),`. The `,_jsx(_components.strong,{children:`Add`}),` button stays disabled until at least one is selected.`]}),_jsx(Note,{children:_jsxs(_components.p,{children:[`A parameter the system couldn’t extract shows `,_jsx(_components.strong,{children:`Empty`}),` and can’t be selected. The uploaded file is deleted immediately after extraction and is not stored in any temporary or permanent location. It is never executed.`]})})]}),_jsx(Step,{title:`Add more files if needed`,children:_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Add another file`}),` to repeat the process. If a newly extracted parameter matches one already in the rule (manually entered or from another file), it’s grouped with OR logic; otherwise it’s added with AND logic. The `,_jsx(_components.strong,{children:`X`}),` next to an uploaded file name removes the file and every parameter it contributed.`]})})]}),_jsx(Frame,{caption:`The Extracted Application Parameters pop-up after uploading a file.`,children:_jsx(OptimizedImage,{src:`https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-file-upload-parameters.png?fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=4fc1309a0c82b6b6a2a2b1854c11d6a6`,alt:`Extracted Application Parameters pop-up with parameter checkboxes`,\"data-og-width\":`1823`,width:`1823`,\"data-og-height\":`933`,height:`933`,\"data-path\":`images/pam/privilege-elevation/rule-file-upload-parameters.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-file-upload-parameters.png?w=280\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=ff69ad76fb06bdc7fe7bc03a07fd28fb 280w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-file-upload-parameters.png?w=560\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=efb8fe47995ad43709ad9d65956fc819 560w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-file-upload-parameters.png?w=840\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=fc07ba8c740b9902217aa98b2cbf8319 840w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-file-upload-parameters.png?w=1100\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=ecb52089902a9941d975c73567d8422b 1100w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-file-upload-parameters.png?w=1650\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=f602ea1321ec7f375bf92bd8a9d975c4 1650w, https://mintcdn.com/syteca/5r-OD6BZ6Hqi3EUs/images/pam/privilege-elevation/rule-file-upload-parameters.png?w=2500\u0026fit=max\u0026auto=format\u0026n=5r-OD6BZ6Hqi3EUs\u0026q=85\u0026s=5a3e3eaa580d1d97a1d46e4b22ff7f4a 2500w`})})]})]}),`\n`,_jsx(Tip,{children:_jsxs(_components.p,{children:[`Once a rule holds five conditions, the tab shows a reminder: `,_jsx(_components.em,{children:`“Use simple rules to reduce rule evaluation time.”`})]})}),`\n`,_jsx(Heading,{level:`4`,id:`extract-parameters-offline`,children:`Extract parameters offline`}),`\n`,_jsxs(_components.p,{children:[`For SaaS customers, or anyone who prefers not to upload files to the Management Tool, the `,_jsx(_components.strong,{children:`Offline Parameters Extractor`}),` is a small, standalone Windows utility you run locally.`]}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`Download and run the tool`,children:_jsxs(_components.p,{children:[_jsx(_components.a,{href:`https://download.syteca.com/Offline_Parameters_Extractor.exe`,children:`Download the Offline Parameters Extractor`}),` and run it on any Windows computer. No installation and no server connection are required.`]})}),_jsx(Step,{title:`Choose a file`,children:_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Browse`}),` and select a `,_jsx(_components.code,{children:`.exe`}),` or `,_jsx(_components.code,{children:`.msi`}),` file.`]})}),_jsx(Step,{title:`Copy the extracted values`,children:_jsxs(_components.p,{children:[`The tool displays `,_jsx(_components.strong,{children:`File hash (SHA-256)`}),`, `,_jsx(_components.strong,{children:`Executable name(s)`}),`, `,_jsx(_components.strong,{children:`Path prefix`}),`, and `,_jsx(_components.strong,{children:`Digital signature`}),`, each with its own `,_jsx(_components.strong,{children:`Copy`}),` button. A field that couldn’t be extracted shows `,_jsx(_components.strong,{children:`Empty`}),`.`]})}),_jsx(Step,{title:`Paste into your rule`,children:_jsx(_components.p,{children:`Paste the copied values into the corresponding manual-entry fields on the Targeting Criteria tab.`})})]}),`\n`,_jsx(Note,{children:_jsx(_components.p,{children:`The tool never uploads or executes the file. It only reads it locally to extract metadata, and isn’t included in the standard server installation package.`})}),`\n`,_jsx(Heading,{level:`3`,id:`4-assign-endpoints`,children:`4. Assign Endpoints`}),`\n`,_jsxs(_components.p,{children:[`Select at least one endpoint or endpoint group. If none is selected, the tab shows: `,_jsx(_components.em,{children:`“At least one Endpoint or Endpoint group must be selected.”`})]}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Section`}),_jsx(_components.th,{children:`Selects`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Domain Computer groups`})}),_jsxs(_components.td,{children:[`A domain (only domains added via an `,_jsx(_components.a,{href:`/administration/integrations/ldap-targets`,children:`LDAP target`}),`), typed into a text box with matching domains suggested as you type, and an Organizational Unit or computer group within it. Multiple values can be selected in the OU / Computers field. Supports `,_jsx(_components.code,{children:`*`}),` as a wildcard for any domain or local computer.`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Endpoints`})}),_jsxs(_components.td,{children:[`Individual endpoints where the Syteca Client is installed, or `,_jsx(_components.strong,{children:`Select All`}),`.`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Endpoint groups`})}),_jsxs(_components.td,{children:[`Existing endpoint groups, or `,_jsx(_components.strong,{children:`Select All`}),`.`]})]})]})]}),`\n`,_jsx(Note,{children:_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Domain Computer groups`}),` combines with `,_jsx(_components.strong,{children:`Endpoints`}),` and `,_jsx(_components.strong,{children:`Endpoint groups`}),` using AND logic, so if you specify a domain group you must also select at least one endpoint or endpoint group. The Domain Computer group field on its own is not mandatory. `,_jsx(_components.strong,{children:`Endpoints`}),` and `,_jsx(_components.strong,{children:`Endpoint groups`}),` combine with each other using OR logic. The PAM Client group can’t be selected here.`]})}),`\n`,_jsxs(_components.p,{children:[`Each added item appears with an `,_jsx(_components.strong,{children:`X`}),` to remove it individually. `,_jsx(_components.strong,{children:`Clear All`}),` appears once a section holds at least one item and removes everything in that section at once.`]}),`\n`,_jsx(Heading,{level:`3`,id:`5-assigned-users`,children:`5. Assigned Users`}),`\n`,_jsxs(_components.p,{children:[`Choose whether the rule applies to everyone, or to specific users. `,_jsx(_components.strong,{children:`All`}),` is selected by default.`]}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Option`}),_jsx(_components.th,{children:`Behavior`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`All`})}),_jsx(_components.td,{children:`Applies to every user on the assigned endpoints.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Selected`})}),_jsxs(_components.td,{children:[`Applies only to the users and user groups in the Users and User Groups grid. Leaving the grid empty shows: `,_jsx(_components.em,{children:`“No users or user groups selected. Add at least one user or user group to continue.”`})]})]})]})]}),`\n`,_jsxs(_components.p,{children:[`Add entries to the grid with `,_jsx(_components.strong,{children:`Add`}),`, then fill both columns:`]}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Column`}),_jsx(_components.th,{children:`Accepts`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Domain / Computer`})}),_jsxs(_components.td,{children:[`A domain added through an LDAP target, or an endpoint where the Client is installed. Domains are listed first, endpoints below them. `,_jsx(_components.code,{children:`*`}),` is supported as a wildcard.`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`User / User group`})}),_jsxs(_components.td,{children:[`Free text with autocomplete. `,_jsx(_components.code,{children:`*`}),` is supported as part of the value, for example `,_jsx(_components.code,{children:`*\\\\Administrator`}),`.`]})]})]})]}),`\n`,_jsxs(_components.p,{children:[`Both columns are mandatory. An empty column shows `,_jsx(_components.em,{children:`“This field is required.”`}),` under the field, and the entry isn’t saved.`]}),`\n`,_jsxs(_components.p,{children:[`Use the tick icon to save a row, the pencil icon to edit it, and the `,_jsx(_components.strong,{children:`X`}),` icon to remove it. `,_jsx(_components.strong,{children:`Remove All`}),` appears once the grid holds at least one entry.`]}),`\n`,_jsx(Note,{children:_jsxs(_components.p,{children:[`Autocomplete queries Active Directory only when a `,_jsx(_components.strong,{children:`Domain`}),` is selected, and returns at most 20 suggestions plus the exact text you typed. Selecting a `,_jsx(_components.strong,{children:`Computer`}),` returns only the typed value, with no directory lookup. Selecting `,_jsx(_components.code,{children:`*`}),` searches across every available domain.`]})}),`\n`,_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Exceptions`}),` are configured the same way, in their own grid, and always override the main selection. A user listed as an exception is excluded from the rule even if they would otherwise match.`]}),`\n`,_jsx(Note,{children:_jsxs(_components.p,{children:[`The Exceptions grid is available with both `,_jsx(_components.strong,{children:`All`}),` and `,_jsx(_components.strong,{children:`Selected`}),`, and may be left empty. To apply a rule to everyone except a few people, choose `,_jsx(_components.strong,{children:`All`}),` and list those people as exceptions. Choosing `,_jsx(_components.strong,{children:`Selected`}),` and filling in only the Exceptions grid is not enough: the Users and User Groups grid still needs at least one entry.`]})}),`\n`,_jsx(Heading,{level:`3`,id:`6-summary`,children:`6. Summary`}),`\n`,_jsxs(_components.p,{children:[`Review every section before saving: Elevation Mode, Targeting Criteria, Assigned Endpoints, Assigned Users (with exceptions). Each section has its own `,_jsx(_components.strong,{children:`Edit`}),` link, which jumps to the matching tab. An `,_jsx(_components.strong,{children:`Impact preview`}),` shows the total number of endpoints the rule will affect.`]}),`\n`,_jsxs(_components.p,{children:[`Where a section holds more than three values, only the first three are listed, followed by a `,_jsx(_components.strong,{children:`+N more`}),` indicator. Clicking it reveals the rest.`]}),`\n`,_jsx(Warning,{children:_jsxs(_components.p,{children:[`If a required setting is missing (for example, `,_jsx(_components.strong,{children:`Require approval`}),` selected with no approver defined), the Summary tab highlights it in a red error block so you can fix it before saving.`]})}),`\n`,_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Save`}),` to activate the rule and return to the Rules page, where it now appears in the grid.`]}),`\n`,_jsx(Heading,{level:`2`,id:`edit-a-rule`,children:`Edit a rule`}),`\n`,_jsxs(_components.p,{children:[`Opening an existing rule for editing starts on the `,_jsx(_components.strong,{children:`Summary`}),` tab, where you can jump to any section via the left navigation or that section’s `,_jsx(_components.strong,{children:`Edit`}),` link. A tab opened through `,_jsx(_components.strong,{children:`Edit`}),` behaves exactly as it does when you navigate to it manually.`]}),`\n`,_jsxs(_components.p,{children:[`Changes are saved as you move between tabs, whether you use the tab navigation or the `,_jsx(_components.strong,{children:`Next`}),` and `,_jsx(_components.strong,{children:`Back`}),` buttons, and `,_jsx(_components.strong,{children:`Save`}),` commits them and closes edit mode. `,_jsx(_components.strong,{children:`Cancel`}),` discards changes made in that session and returns you to the Rules page. Mandatory fields left empty block saving and are highlighted.`]}),`\n`,_jsx(Heading,{level:`2`,id:`how-rules-are-matched`,children:`How rules are matched`}),`\n`,_jsxs(_components.p,{children:[`When a user runs something that triggers elevation, Syteca evaluates every `,_jsx(_components.strong,{children:`enabled`}),` rule and works out which ones apply to the current context. A rule is matched only if all of the following hold:`]}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`The rule is enabled.`}),`\n`,_jsx(_components.li,{children:`Its endpoint and user targeting covers the endpoint and the user.`}),`\n`,_jsx(_components.li,{children:`Its targeting criteria match the application, whether entered manually or extracted from a file.`}),`\n`,_jsx(_components.li,{children:`Its schedule constraints, if configured, are satisfied.`}),`\n`]}),`\n`,_jsx(Heading,{level:`3`,id:`how-conflicting-rules-resolve`,children:`How conflicting rules resolve`}),`\n`,_jsxs(_components.p,{children:[`If more than one enabled rule matches the same elevation attempt, Syteca doesn’t pick a rule arbitrarily. It applies the `,_jsx(_components.strong,{children:`most restrictive matching decision`}),`, in this order:`]}),`\n`,_jsxs(_components.ol,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Deny`}),` (most restrictive)`]}),`\n`,_jsx(_components.li,{children:_jsx(_components.strong,{children:`Require approval`})}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Auto-elevate`}),` (least restrictive)`]}),`\n`]}),`\n`,_jsx(_components.p,{children:`In other words: if even one matched rule says Deny, the result is Deny, regardless of what any other matched rule allows. If none say Deny but at least one says Require approval, the result is Require approval. Only if every matched rule says Auto-elevate does the attempt actually auto-elevate.`}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Rule A`}),_jsx(_components.th,{children:`Rule B`}),_jsx(_components.th,{children:`Result`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsxs(_components.td,{children:[`Auto-elevate for `,_jsx(_components.code,{children:`notepad.exe`})]}),_jsxs(_components.td,{children:[`Deny for `,_jsx(_components.code,{children:`notepad.exe`})]}),_jsx(_components.td,{children:_jsx(_components.strong,{children:`Deny`})})]}),_jsxs(_components.tr,{children:[_jsxs(_components.td,{children:[`Auto-elevate for `,_jsx(_components.code,{children:`mmc.exe`})]}),_jsxs(_components.td,{children:[`Require approval for `,_jsx(_components.code,{children:`mmc.exe`})]}),_jsx(_components.td,{children:_jsx(_components.strong,{children:`Require approval`})})]}),_jsxs(_components.tr,{children:[_jsxs(_components.td,{children:[`Auto-elevate for `,_jsx(_components.code,{children:`cmd.exe`})]}),_jsxs(_components.td,{children:[`Auto-elevate for `,_jsx(_components.code,{children:`cmd.exe`}),`, different targeting`]}),_jsx(_components.td,{children:_jsx(_components.strong,{children:`Auto-elevate`})})]})]})]}),`\n`,_jsx(Heading,{level:`2`,id:`what-happens-when-the-client-starts-enforcing-a-rule`,children:`What happens when the Client starts enforcing a rule`}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`No changes until the first rule is saved`,children:_jsx(_components.p,{children:`After installing the Syteca Client, nothing changes on the endpoint until you save an enabled Privilege Elevation rule targeting it.`})}),_jsx(Step,{title:`UAC is intercepted, not removed`,children:_jsx(_components.p,{children:`Once a rule is active, the Syteca Client enforces Windows UAC settings so that elevation always triggers a prompt, making silent unmanaged elevation impossible, and intercepts that prompt before it completes to evaluate your rules against it.`})}),_jsx(Step,{title:`Group membership is untouched`,children:_jsx(_components.p,{children:`Privilege Elevation does not remove any user from the local Administrators group. It governs how elevation happens, not who’s technically capable of it.`})})]}),`\n`,_jsx(Note,{children:_jsx(_components.p,{children:`Upgrading to a version with Privilege Elevation adds the new page and rules to the Management Tool but changes nothing by default. The native Windows UAC continues to work exactly as before until you create and enable your first rule.`})}),`\n`,_jsx(Heading,{level:`3`,id:`windows-uac-policies-that-privilege-elevation-changes`,children:`Windows UAC policies that Privilege Elevation changes`}),`\n`,_jsx(_components.p,{children:`To guarantee that every elevation attempt produces a prompt it can intercept, the Syteca Client sets four Windows UAC security policies on the endpoint:`}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Policy`}),_jsx(_components.th,{children:`Value Syteca sets`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`User Account Control: Run all administrators in Admin Approval Mode`})}),_jsx(_components.td,{children:_jsx(_components.strong,{children:`Enabled`})})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`User Account Control: Behavior of the elevation prompt for administrators in Admin Approval Mode`})}),_jsx(_components.td,{children:_jsx(_components.strong,{children:`Prompt for credentials on the secure desktop`})})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`User Account Control: Behavior of the elevation prompt for standard users`})}),_jsx(_components.td,{children:_jsx(_components.strong,{children:`Prompt for credentials on the secure desktop`})})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`User Account Control: Admin Approval Mode for the Built-in Administrator account`})}),_jsx(_components.td,{children:_jsx(_components.strong,{children:`Enabled`})})]})]})]}),`\n`,_jsxs(_components.p,{children:[`These policies live under `,_jsx(_components.strong,{children:`Security Settings → Local Policies → Security Options`}),` in Local Security Policy or Group Policy.`]}),`\n`,_jsx(Warning,{children:_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`A change to “Run all administrators in Admin Approval Mode” takes effect only after the endpoint restarts.`}),` Windows enables this policy by default, so endpoints where it has never been changed need no action. On endpoints where it has been disabled, Syteca sets it back to `,_jsx(_components.strong,{children:`Enabled`}),`, and that endpoint must be rebooted before Privilege Elevation rules are enforced on it.`]})}),`\n`,_jsx(Tip,{children:_jsx(_components.p,{children:`Review these four settings on your target endpoints before you deploy Privilege Elevation. If your organization has changed any of them away from the Windows defaults, include a reboot window in your rollout plan so the rules take effect when you expect them to.`})}),`\n`,_jsx(Heading,{level:`2`,id:`multi-tenant-and-high-availability`,children:`Multi-tenant and high availability`}),`\n`,_jsxs(_components.p,{children:[`In `,_jsx(_components.a,{href:`/administration/multi-tenant/overview`,children:`multi-tenant mode`}),`, the Privilege Elevation page is added to every tenant, and rule evaluation works the same way for a non-default tenant as for the default one.`]}),`\n`,_jsx(Heading,{level:`2`,id:`related`,children:`Related`}),`\n`,_jsxs(CardGroup,{cols:2,children:[_jsx(Card,{title:`Overview`,icon:`shield-check`,href:`/pam/privilege-elevation/overview`,children:_jsx(_components.p,{children:`What Privilege Elevation does and how it’s licensed.`})}),_jsx(Card,{title:`Events and monitoring`,icon:`activity`,href:`/pam/privilege-elevation/events`,children:_jsx(_components.p,{children:`Every elevation decision, logged and searchable.`})}),_jsx(Card,{title:`End-user experience`,icon:`monitor`,href:`/pam/privilege-elevation/end-user-experience`,children:_jsx(_components.p,{children:`What a user sees when a rule applies to them.`})}),_jsx(Card,{title:`Add a secret`,icon:`key-round`,href:`/pam/secrets/add-secret`,children:_jsx(_components.p,{children:`Create the Secret a Require approval or Auto-elevate rule uses.`})})]})]})}function MDXContent(props={}){const{wrapper:MDXLayout}={..._provideComponents(),...props.components};return MDXLayout?_jsx(MDXLayout,{...props,children:_jsx(_createMdxContent,{...props})}):_createMdxContent(props)}return{default:MDXContent};function _missingMdxReference(id,component){throw new Error(`Expected `+(component?`component`:`object`)+\" `\"+id+\"` to be defined: you likely forgot to import, pass, or provide it.\")}","frontmatter":{},"scope":{"codeStyling":"system","config":{},"pageMetadata":{"title":"Creating and Managing Privilege Elevation Rules","sidebarTitle":"Rules","description":"Build Privilege Elevation rules that decide when a Windows application should Auto-elevate, require approval, or be denied. It includes targeting criteria, endpoints, users, and how conflicting rules resolve.","icon":"list-checks","keywords":["syteca privilege elevation rules","auto-elevate require approval deny","pedm targeting criteria","offline parameters extractor","syteca uac rule priority","uac admin approval mode","privilege elevation uac policy reboot"],"href":"/pam/privilege-elevation/rules"}}},"mdxSourceWithNoJs":null},"mdxExtracts":{"tableOfContents":[{"title":"The Rules page","slug":"the-rules-page","depth":2,"children":[{"title":"The rules grid","slug":"the-rules-grid","depth":3,"children":[]},{"title":"Bulk actions","slug":"bulk-actions","depth":3,"children":[]}]},{"title":"Create a rule","slug":"create-a-rule","depth":2,"children":[{"title":"1. Details","slug":"1-details","depth":3,"children":[]},{"title":"2. Elevation Mode","slug":"2-elevation-mode","depth":3,"children":[]},{"title":"How the Secret is chosen","slug":"how-the-secret-is-chosen","depth":4,"children":[]},{"title":"3. Targeting Criteria","slug":"3-targeting-criteria","depth":3,"children":[]},{"title":"Extract parameters offline","slug":"extract-parameters-offline","depth":4,"children":[]},{"title":"4. Assign Endpoints","slug":"4-assign-endpoints","depth":3,"children":[]},{"title":"5. Assigned Users","slug":"5-assigned-users","depth":3,"children":[]},{"title":"6. Summary","slug":"6-summary","depth":3,"children":[]}]},{"title":"Edit a rule","slug":"edit-a-rule","depth":2,"children":[]},{"title":"How rules are matched","slug":"how-rules-are-matched","depth":2,"children":[{"title":"How conflicting rules resolve","slug":"how-conflicting-rules-resolve","depth":3,"children":[]}]},{"title":"What happens when the Client starts enforcing a rule","slug":"what-happens-when-the-client-starts-enforcing-a-rule","depth":2,"children":[{"title":"Windows UAC policies that Privilege Elevation changes","slug":"windows-uac-policies-that-privilege-elevation-changes","depth":3,"children":[]}]},{"title":"Multi-tenant and high availability","slug":"multi-tenant-and-high-availability","depth":2,"children":[]},{"title":"Related","slug":"related","depth":2,"children":[]}],"codeExamples":{}},"jsLinks":[],"subdomain":"syteca","siteName":"Syteca","title":"Creating and Managing Privilege Elevation Rules - Syteca","navMaps":{"firstHrefInVersion":{},"firstHrefInLanguage":{}},"lastModified":"2026-11-18T02:45:20.327Z","originalFileLocation":"pam/privilege-elevation/rules.mdx"},"headHtml":"\u003cscript data-mint-head>(function(){var d=document.documentElement,p=null;if(!p){try{p=localStorage.getItem(\"isDarkMode\")}catch(e){}if(p==='true')p='dark';else if(p==='false')p='light';if(p!=='light'\u0026\u0026p!=='dark'\u0026\u0026p!=='system')p=\"system\"}var r=p==='system'?(matchMedia(\"(prefers-color-scheme: dark)\").matches?'dark':'light'):p;d.classList.remove(r==='dark'?'light':'dark');d.classList.add(r);d.setAttribute(\"data-theme-preference\",p)})();\u003c/script>\u003cmeta data-mint-head name=\"description\" content=\"Build Privilege Elevation rules that decide when a Windows application should Auto-elevate, require approval, or be denied. It includes targeting criteria, endpoints, users, and how conflicting rules resolve.\">\u003cmeta data-mint-head name=\"application-name\" content=\"Syteca\">\u003cmeta data-mint-head name=\"generator\" content=\"Mintlify\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon/android-chrome-192x192.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"apple-touch-icon\" type=\"image/png\" sizes=\"180x180\" href=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon/apple-touch-icon.png\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon/favicon-16x16.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon/favicon-32x32.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon/favicon.ico\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon-dark/android-chrome-192x192.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon-dark/favicon-16x16.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon-dark/favicon-32x32.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon-dark/favicon.ico\" media=\"(prefers-color-scheme: dark)\">\u003cmeta data-mint-head property=\"og:title\" content=\"Creating and Managing Privilege Elevation Rules - Syteca\">\u003cmeta data-mint-head property=\"og:description\" content=\"Build Privilege Elevation rules that decide when a Windows application should Auto-elevate, require approval, or be denied. It includes targeting criteria, endpoints, users, and how conflicting rules resolve.\">\u003cmeta data-mint-head property=\"og:site_name\" content=\"Syteca Docs\">\u003cmeta data-mint-head property=\"og:url\" content=\"https://www.syteca.com/docs/pam/privilege-elevation/rules\">\u003cmeta data-mint-head property=\"og:type\" content=\"website\">\u003cmeta data-mint-head property=\"og:image\" content=\"https://www.syteca.com/og-default.png\">\u003cmeta data-mint-head property=\"og:image:width\" content=\"1200\">\u003cmeta data-mint-head property=\"og:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"twitter:card\" content=\"summary_large_image\">\u003cmeta data-mint-head name=\"twitter:title\" content=\"Creating and Managing Privilege Elevation Rules - Syteca\">\u003cmeta data-mint-head name=\"twitter:description\" content=\"Build Privilege Elevation rules that decide when a Windows application should Auto-elevate, require approval, or be denied. It includes targeting criteria, endpoints, users, and how conflicting rules resolve.\">\u003cmeta data-mint-head name=\"twitter:image\" content=\"https://www.syteca.com/og-default.png\">\u003cmeta data-mint-head name=\"twitter:image:width\" content=\"1200\">\u003cmeta data-mint-head name=\"twitter:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"msapplication-config\" content=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon/browserconfig.xml\">\u003cmeta data-mint-head name=\"apple-mobile-web-app-title\" content=\"Syteca\">\u003cmeta data-mint-head name=\"msapplication-TileColor\" content=\"#2563EB\">\u003clink data-mint-head rel=\"canonical\" href=\"https://www.syteca.com/docs/pam/privilege-elevation/rules\">\u003clink data-mint-head rel=\"alternate\" type=\"application/xml\" href=\"/docs/sitemap.xml\">\u003clink data-mint-head rel=\"alternate\" type=\"text/markdown\" href=\"/docs/pam/privilege-elevation/rules.md\">\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@graph\":[{\"@type\":\"Organization\",\"@id\":\"https://www.syteca.com/#organization\",\"name\":\"Syteca\",\"url\":\"https://www.syteca.com\",\"logo\":{\"@type\":\"ImageObject\",\"url\":\"https://mintcdn.com/syteca/ZVta4JfIcSnC47NX/logo/syteca-light.svg?fit=max\u0026auto=format\u0026n=ZVta4JfIcSnC47NX\u0026q=85\u0026s=154a18f69aa4aefa55de0de7669934c7\"}},{\"@type\":\"WebSite\",\"@id\":\"https://www.syteca.com/docs#website\",\"name\":\"Syteca\",\"url\":\"https://www.syteca.com/docs\",\"publisher\":{\"@id\":\"https://www.syteca.com/#organization\"}},{\"@type\":\"WebPage\",\"@id\":\"https://www.syteca.com/docs/pam/privilege-elevation/rules#webpage\",\"url\":\"https://www.syteca.com/docs/pam/privilege-elevation/rules\",\"name\":\"Creating and Managing Privilege Elevation Rules\",\"description\":\"Build Privilege Elevation rules that decide when a Windows application should Auto-elevate, require approval, or be denied. It includes targeting criteria, endpoints, users, and how conflicting rules resolve.\",\"dateModified\":\"2026-11-18T02:45:20.327Z\",\"isPartOf\":{\"@id\":\"https://www.syteca.com/docs#website\"},\"breadcrumb\":{\"@id\":\"https://www.syteca.com/docs/pam/privilege-elevation/rules#breadcrumb\"}},{\"@type\":\"BreadcrumbList\",\"@id\":\"https://www.syteca.com/docs/pam/privilege-elevation/rules#breadcrumb\",\"itemListElement\":[{\"@type\":\"ListItem\",\"position\":1,\"name\":\"Privilege Elevation\",\"item\":\"https://www.syteca.com/docs/pam/privilege-elevation/overview\"},{\"@type\":\"ListItem\",\"position\":2,\"name\":\"Creating and Managing Privilege Elevation Rules\",\"item\":\"https://www.syteca.com/docs/pam/privilege-elevation/rules\"}]},{\"@type\":[\"Article\",\"TechArticle\"],\"@id\":\"https://www.syteca.com/docs/pam/privilege-elevation/rules#article\",\"headline\":\"Creating and Managing Privilege Elevation Rules\",\"name\":\"Creating and Managing Privilege Elevation Rules\",\"description\":\"Build Privilege Elevation rules that decide when a Windows application should Auto-elevate, require approval, or be denied. It includes targeting criteria, endpoints, users, and how conflicting rules resolve.\",\"url\":\"https://www.syteca.com/docs/pam/privilege-elevation/rules\",\"mainEntityOfPage\":{\"@id\":\"https://www.syteca.com/docs/pam/privilege-elevation/rules#webpage\"},\"image\":\"https://www.syteca.com/og-default.png\",\"dateModified\":\"2026-11-18T02:45:20.327Z\",\"keywords\":\"syteca privilege elevation rules, auto-elevate require approval deny, pedm targeting criteria, offline parameters extractor, syteca uac rule priority, uac admin approval mode, privilege elevation uac policy reboot\",\"publisher\":{\"@id\":\"https://www.syteca.com/#organization\"},\"isPartOf\":{\"@id\":\"https://www.syteca.com/docs#website\"}}]}\u003c/script>\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@type\":\"WebSite\",\"name\":\"Syteca\",\"publisher\":{\"@type\":\"Organization\",\"name\":\"Syteca\"},\"provider\":{\"@type\":\"Organization\",\"name\":\"Mintlify\",\"url\":\"https://mintlify.com\"}}\u003c/script>","agentPointerHref":"/docs/pam/privilege-elevation/rules.md","siteName":"Syteca","nav":{"global":null,"tabs":[{"tab":"Get Started","pages":[{"title":"Get Started","href":"/get-started/what-is-syteca"}]},{"tab":"Session Monitoring","pages":[{"title":"Session Monitoring","href":"/session-monitoring/overview"}]},{"tab":"Privileged Access Management","groups":[{"group":"Overview","pages":[{"title":"Syteca Privileged Access Management (PAM) Overview","sidebarTitle":"Overview","icon":"lock","href":"/pam/overview"}]},{"group":"Access","pages":[{"title":"Web Connection Manager: Agentless PAM in a Browser","sidebarTitle":"Web Connection Manager","icon":"globe","href":"/pam/access/web-connection-manager"},{"title":"Syteca PAM Connection Manager for Linux","sidebarTitle":"Linux PAM Connection Manager","icon":"terminal","href":"/pam/access/linux-pacm"},{"title":"Desktop Connection Manager","sidebarTitle":"Desktop Connection Manager","icon":"monitor","href":"/pam/access/desktop-connection-manager"},{"title":"Manage Access Requests","sidebarTitle":"Access requests","icon":"inbox","href":"/pam/access/access-requests"}]},{"group":"Account Discovery","pages":[{"title":"Discover and Onboard Privileged Accounts in Syteca","sidebarTitle":"Overview","icon":"radar","href":"/pam/discovery/overview"},{"title":"Configure WMI and PowerShell for Computer Discovery","sidebarTitle":"WMI \u0026 PowerShell scanning","icon":"scan-search","href":"/pam/discovery/wmi-powershell"},{"title":"Configure SSH Connections for Linux Discovery","sidebarTitle":"SSH for Linux Discovery","icon":"terminal","href":"/pam/discovery/ssh-linux-scanning"},{"title":"Service Account Dependency Discovery and Onboarding","sidebarTitle":"Service Account Dependencies","icon":"network","href":"/pam/discovery/service-account-dependencies"}]},{"group":"Secrets \u0026 Password Management","pages":[{"title":"Set Up Password Management","sidebarTitle":"Set up Password Management","icon":"sliders-horizontal","href":"/pam/secrets/configure-password-management"},{"title":"Add a Secret","sidebarTitle":"Add a secret","icon":"key-round","href":"/pam/secrets/add-secret"},{"title":"Permissions for Secrets","sidebarTitle":"Permissions","icon":"users","href":"/pam/secrets/permissions"},{"title":"View and Manage Secrets and Folders","sidebarTitle":"View \u0026 manage secrets","icon":"folder-tree","href":"/pam/secrets/view-manage-secrets"},{"title":"Connect to Privileged Accounts Using a Secret","sidebarTitle":"Connect using a secret","icon":"plug-zap","href":"/pam/secrets/use-secrets"},{"title":"View and Copy a Secret's Password","sidebarTitle":"View \u0026 copy password","icon":"eye","href":"/pam/secrets/view-copy-password"},{"title":"Password Checkout","sidebarTitle":"Password checkout","icon":"user-lock","href":"/pam/secrets/password-checkout"},{"title":"Remote Password and SSH Key Rotation","sidebarTitle":"Password rotation","icon":"refresh-cw","href":"/pam/secrets/remote-password-rotation"},{"title":"Heartbeat Checking","sidebarTitle":"Heartbeat Checking","icon":"activity","href":"/pam/secrets/heartbeat"},{"title":"Transfer Files over SFTP with WinSCP via Syteca PAM","sidebarTitle":"File transfer","icon":"file-up","href":"/pam/secrets/file-transfer"},{"title":"Workforce Password Management","sidebarTitle":"Workforce Password Management","icon":"user-cog","href":"/pam/secrets/workforce-password-management"},{"title":"Edit a Secret","sidebarTitle":"Edit a secret","icon":"pen-line","href":"/pam/secrets/edit-secret"},{"title":"Delete a Secret","sidebarTitle":"Delete a secret","icon":"trash-2","href":"/pam/secrets/delete-secret"}]},{"group":"Privilege Elevation","pages":[{"title":"Syteca Privilege Elevation","sidebarTitle":"Overview","description":"Control when and how administrator privileges are used on Windows endpoints and replace the native UAC prompt with policy-driven Auto-elevate, Require approval, or Deny decisions, all logged.","icon":"shield-check","href":"/pam/privilege-elevation/overview"},{"title":"Creating and Managing Privilege Elevation Rules","sidebarTitle":"Rules","icon":"list-checks","href":"/pam/privilege-elevation/rules"},{"title":"Events and Monitoring","sidebarTitle":"Events","description":"The full audit trail of every Privilege Elevation decision. Auto-elevate, Require approval, and Deny plus how session recording behaves depending on your Syteca license.","icon":"activity","href":"/pam/privilege-elevation/events"},{"title":"End-User Experience","sidebarTitle":"End-User Experience","icon":"monitor","href":"/pam/privilege-elevation/end-user-experience"}]}]},{"tab":"Endpoint Risk Control","pages":[{"title":"Endpoint Risk Control","href":"/risk/overview"}]},{"tab":"Administration","pages":[{"title":"Administration","href":"/administration/overview"}]},{"tab":"API \u0026 Integrations","pages":[{"title":"API \u0026 Integrations","href":"/api/overview"}]},{"tab":"Release Notes","pages":[{"title":"Release Notes","href":"/release-notes/overview"}]},{"tab":"Resources","pages":[{"title":"Resources","href":"/resources/overview"}]}]},"basePath":"","title":"Creating and Managing Privilege Elevation Rules - Syteca","deploymentId":"dpl_J2QdBVuN65x4CCtpqPb371YPt4xi","buildId":"dpl_J2QdBVuN65x4CCtpqPb371YPt4xi","dynamics":["07c022d89b","a74be98ba7"],"chunks":["Frame-LlRejYWv.js","DynamicMarkdown-DzuINhDe.js","zoom-image-lightbox-B0JqbMuR.js","lightbox-handle-r17bVUz3.js"]}