Syteca user management: three user types (internal, Active Directory, application account), five default user groups, custom groups, per-Endpoint permission scoping, two-factor authentication, and admin hardening.
Every security platform has user roles. Most do the minimum: admin, operator, viewer, maybe a custom role tier and call it RBAC. That works until you’re running a real PAM and User Activity Monitoring deployment, at which point you need to express things like: “Sarah can view monitoring results for the Finance Endpoint group but not Engineering, can’t see clipboard text, can approve One-Time Password requests, can’t disable the default admin, and her permissions inherit from the Supervisors user group except when overridden by her own grants.” Generic RBAC doesn’t fit that shape; you either over-grant and hope, or you write workarounds.Competitors at this layer handle similar problems with their own permission models, but with varying granularity. Syteca’s permission model is built around exactly the operations a UAM/PAM admin needs: administrative permissions that gate platform-wide actions, Endpoint permissions that gate per-Endpoint operations, User-to-User access scoping for restricting which endpoint users’ monitoring results a Management Tool user can see, and three user types (internal, Active Directory, application account) that share the same permission engine.
Use Syteca user management when you need to:
Implement separation of duties between platform admins, investigators, and operations staff — with permissions granular enough to express the real boundaries.
Inherit AD user groups automatically — domain group → Management Tool user group → user, so new hires get correct access on day one.
Restrict which endpoint users a given investigator can monitor (the “User-to-User” model) — useful for legal-team segmentation, regional separation, or contractor isolation.
Scope an investigator to only the sessions where an alert fired, so granting access to one incident doesn’t grant access to everything else recorded on that endpoint — see Which sessions a user can see.
Enforce 2FA per user — TOTP via any authenticator app — with admin-managed reset for lost devices.
Harden the default admin by disabling it entirely once other Administrators are configured — eliminates the “default admin compromise” attack surface.
Wire applications into Syteca via Application Account users through the Application Credentials Broker for service-to-service automation.
Pair it with Smart card access — RBAC scopes what a user can do; smart card access scopes who can authenticate as that user. Defense in depth.
All user and user group management requires the administrative User Management permission. In Multi-Tenant mode, users and user groups are completely independent per tenant.
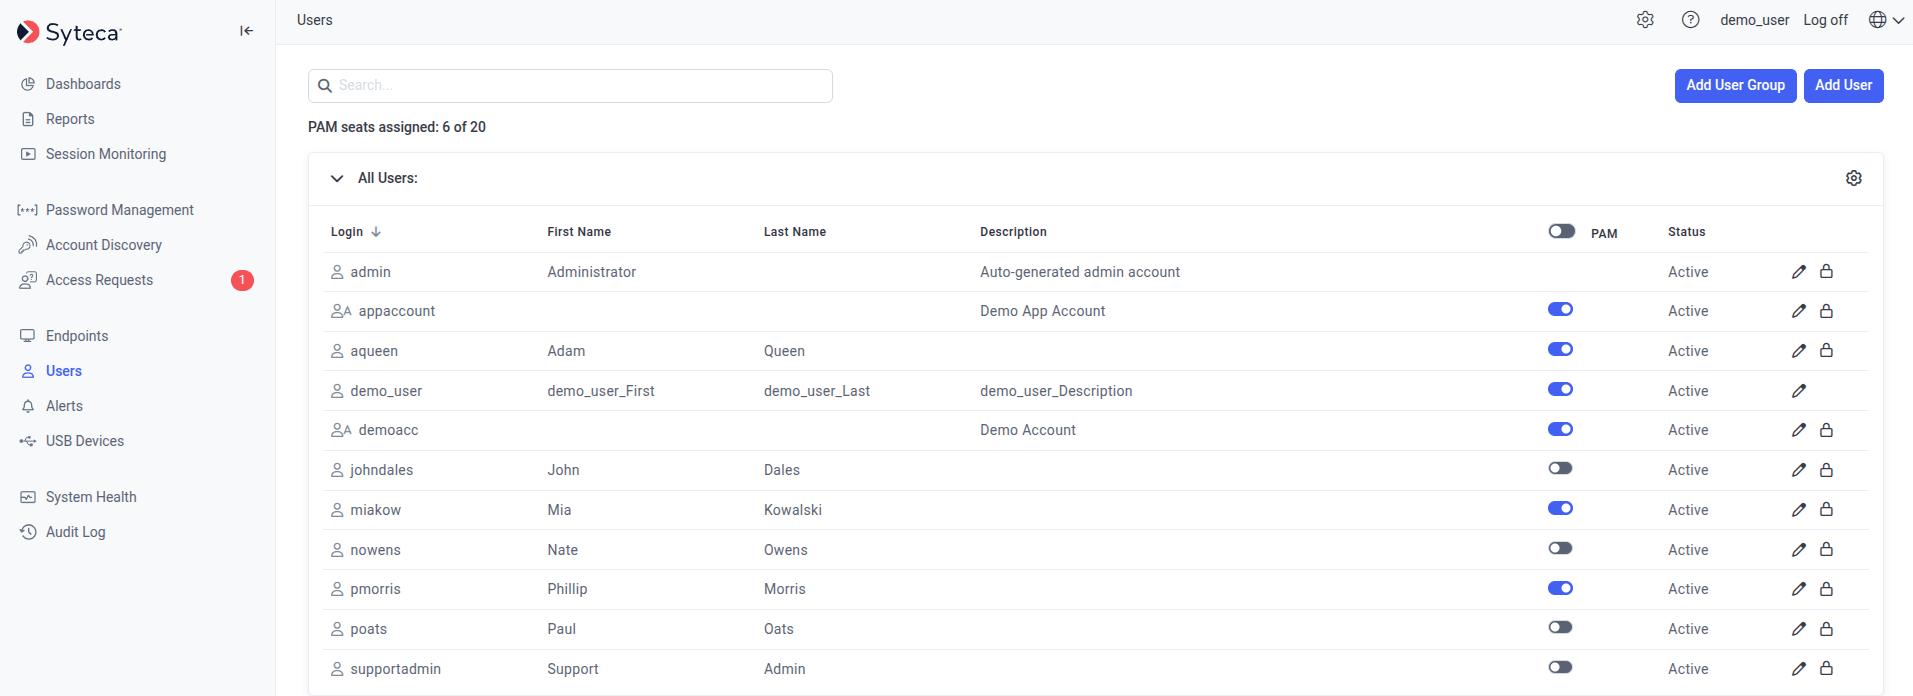
By default, Syteca ships with one administrator — login admin, password set during Application Server installation. The default admin has every permission required to work with the system and is the technician in Multi-Tenant mode, with the ability to create tenants. Once another admin is configured, the default admin can be disabled to harden the deployment.
Local Management Tool accounts are most common for small deployments or for break-glass admin accounts. Authenticate with username + password defined in Syteca.
Active Directory
Domain users and domain user groups are most common for enterprise deployments. Authenticate with AD credentials. Requires an LDAP target configured.
A user can belong to multiple user groups. When a user is in a group:
They inherit every permission granted to that group.
Inherited permissions can only be removed by removing the user from the group they can’t be revoked individually on the user.
The user can also have their own permissions in addition to inherited ones.
If an Active Directory user is added as an independent internal user and as a member of a Windows domain user group, the user’s own permissions take priority over the domain-group-inherited ones.For a worked example of how user-level and group-level permissions combine, see Example of permissions.
On the Users page, click Add User in the top right.
2
Pick the user type
On the User Type tab of the Adding New User page, click one:
Add an Internal User will create a local Management Tool account.
Add an Active Directory User / User Group will add an existing AD user or user group.
Add Application Account will create an account for the ACB API. Not available in SaaS.
Active Directory users / user groups can’t be added if no LDAP target has been configured for the domain, or if the domain is currently unavailable.
If an Active Directory user already belongs to two or more AD user groups in Syteca, that user can’t add themselves as an independent user — only other administrators with appropriate permissions can.
3
Fill in user details
On the User Details tab, complete the form depending on user type:
Internal user
Active Directory user/group
Application Account
Login must be unique. (In Multi-Tenant mode, users of different tenants can share the same login.)
Password at least 8 characters, with at least one lowercase letter, one uppercase letter, one numeric character, and one special character. Cannot contain more than 3 consecutive identical characters or the user’s login name.
First Name / Last Name / Description optional, max 200 characters each.
Email is required for the user to receive an automatically generated one-time password.
Enable two-factor authentication on login force the user to set up TOTP 2FA on first sign-in.
User / User Group will search across any configured domain and select.
Enable two-factor authentication on login force 2FA in addition to AD authentication.
Login — name of the application account.
Client ID / Client Secret authentication — the Client ID is generated automatically and can’t be edited. Add one or more Client Secrets for the applications that will call the API.
Internal and Active Directory users can also call the ACB API. Enable Allow this user account to be used by external applications in the Application Account Settings section of this tab, and the same Client ID / Client Secret and Refresh Token sections appear. See Set up a user account.
Click Next.
4
Assign user groups
On the User Groups tab, select the groups this user will belong to. Click Next.
The user is automatically added to the All Users default group — this can’t be changed.
5
Set administrative permissions
On the Administrative Permissions tab, select the administrative permissions to grant the user directly (in addition to any inherited from groups).
You can only add new permissions on top of group-inherited ones. To remove inherited permissions, remove the user from the relevant group.
Click Next.
6
Set Endpoint access
On the Endpoint Access tab, for each Endpoint or Endpoint group:
Two of these permissions decide which sessions the user can see: Viewing All Monitoring Results reveals every session on the Endpoint, and Viewing Alerted Sessions reveals only those containing a triggered alert. Neither lets the user open a session on its own. See Which sessions a user can see.
Use the Search box + Apply Filters button at the top to find specific Endpoints or groups by name.
Click Next.
7
(Optional) Set User-to-User access
On the User Access tab, restrict which endpoint users’ monitoring results this Management Tool user can see. If you leave this empty, the user sees sessions for all endpoint users they have Viewing Monitoring Results permission for.To restrict:
Click Add User on the right.
Pick the Domain / Computer Name and User / User Group from the drop-downs. Use * as a wildcard.
Click the Add icon to commit.
The drop-downs only show domains, computers, users, and groups already seen by Syteca during monitoring — but you can also type new names directly.
Settings here apply to all sessions for the added endpoint users — past and future. Exception: if you add a domain group, only sessions recorded after adding the group are accessible.
On the Users page, click the Edit User icon next to the user.
2
Make your changes
Edit the user details, group memberships, permissions, Endpoint access, and User-to-User access on the corresponding tabs — same as when adding a user.
3
Reset 2FA (if needed)
A Reset 2FA button appears next to the Enable two-factor authentication on login checkbox — but only after the user has already signed in and set up 2FA, and only for the tenant admin and Management Tool users with the User Management permission. Click it to delete the user’s 2FA profile, useful when the user has lost both their phone and their 2FA recovery code.
4
Save
Click Finish to save and exit, or Next to save progressively across tabs.
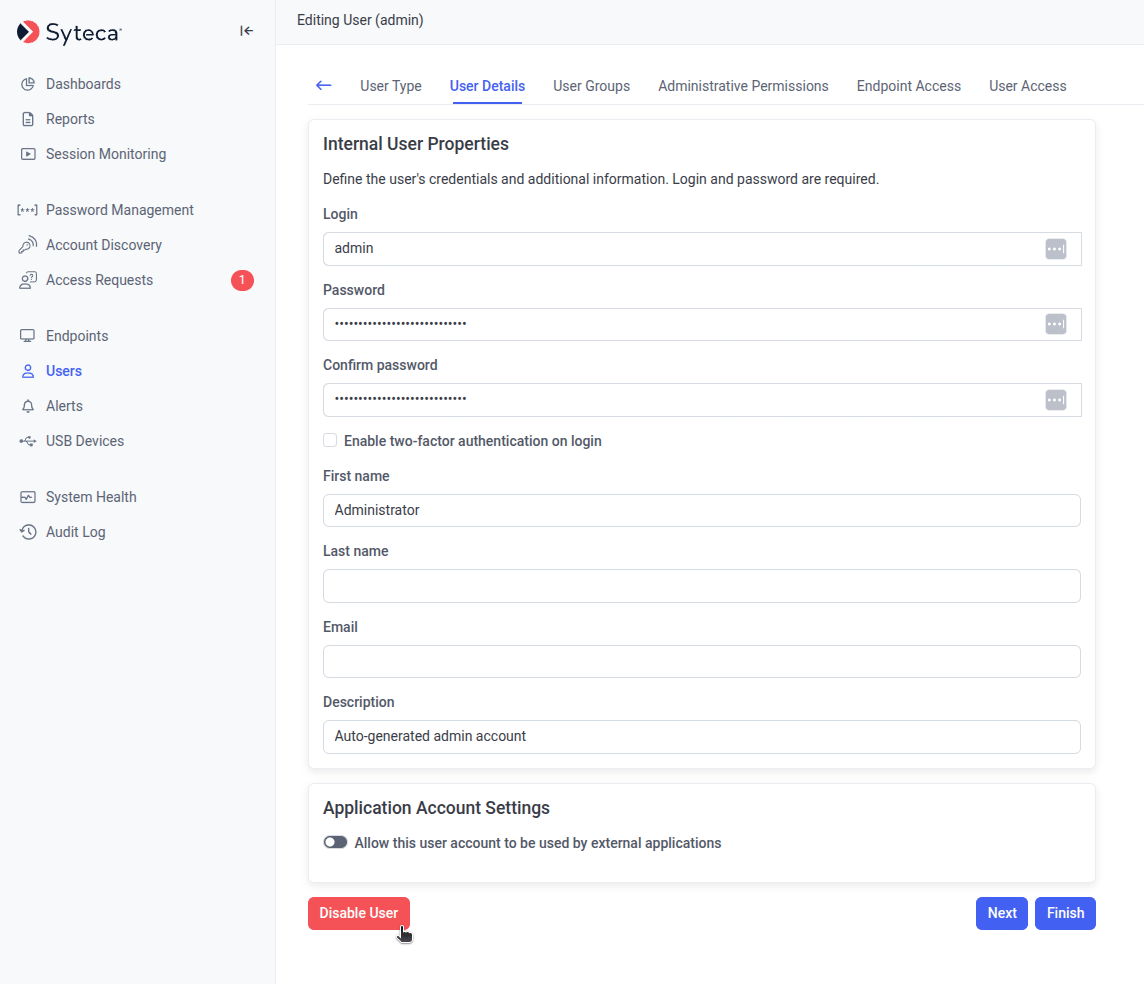
The Delete User button appears in the bottom left when editing — see Delete a user below. For the default admin user, the Disable User button replaces Delete User — see Disable the default admin.
Deleting a user means they immediately lose access to the system. If they’re signed in at the moment of deletion, the Management Tool becomes unavailable immediately and pages stop loading.
1
Open the user
Click the Edit User icon next to the user on the Users page.
2
Delete
On the User Details tab, click Delete User in the bottom left.
The default admin user has unrestricted access to everything in Syteca — useful for initial setup, a meaningful risk during operation. After initial deployment, security-conscious organizations disable the default admin entirely and rely on other Administrators users (each with auditable, configurable permissions) to operate the platform.
On the default admin user's Edit page, the Disable User button replaces the Delete User button - and only appears when another Administrators-group user exists.
Why disable the default admin?
Eliminates a known, high-value credential target (the literal admin account).
Forces all administrative actions through accounts that show up in the Audit log by name.
Meets compliance frameworks (NIST 800-53 IA-4, ISO 27001 A.9.2) that restrict generic admin accounts.
Required by some Pseudonymizer / regulatory deployment patterns.
Before disabling the default admin, at least one other user must be added to the Administrators user group — either as an internal user, an AD user, or via membership in an AD user group added to Administrators.Additionally, the default admin can’t be disabled while they’re the sole owner of certain options or rules. Address these first:
Add another user to Users who can approve access on the Additional Options tab of the USB rule.
If the default admin is the owner (i.e. created) of a Scheduled Report rule, disabling the default admin stops the rule from running and removes it from the Scheduled Reports tab. To preserve the rule, transfer ownership before disabling — or recreate the rule under another user.
Sign in to the Management Tool as any user in the Administrators group except the default admin.
Only users in the default Administrators user group (internal or AD, or AD user-group members) can disable the default admin.
2
Open the default admin
Click Users in the left navigation. Click the Edit User icon next to the default admin user.
3
Click Disable User
On the User Details tab, click Disable User in the bottom left.
The Disable User button replaces Delete User for the default admin. It only appears if at least one other user has been added to the Administrators group.
4
Confirm
Click Confirm in the warning pop-up. If the default admin is the sole owner of any options/rules listed in the prerequisites table, the Confirm button won’t be available — resolve those first.
After the default admin is disabled, the last remaining user in the Administrators group cannot be deleted — Syteca preserves at least one administrator.
The Enable De-Anonymization Password section is hidden on the Pseudonymization configuration tab. If the password was set before disabling, it continues to function but cannot be deselected or changed until the default admin is re-enabled.
The default admin’s API key can no longer be used for API requests. Use the API key of any Administrators-group user instead. Note: Data Connector v.1.9 installation still requires the default admin credentials, so install before disabling.
If the default admin was in the Send email notifications about new accounts found to field of an Account Discovery rule, they’re removed from it and no longer receive notifications.
User groups work the same way as users — same Endpoint Access, same Administrative Permissions, same User-to-User access mechanism. Users in a group inherit the group’s permissions.
1
Open Add User Group
On the Users page, click Add User Group in the top right.
2
Set group properties
On the Group Properties tab, enter a Name (optionally a description), then click Next.
3
Add members
On the Management Tool Users tab, click Add Users in the top left, select the users to add, then click Next.
4
Set administrative permissions
On the Administrative Permissions tab, select the administrative permissions all group members will inherit. Click Next.
5
Set Endpoint access
On the Endpoint Access tab, for each Endpoint or Endpoint group, click the Edit Permissions icon and select the Endpoint permissions to grant. Click Save after each, then Next.
6
(Optional) Set User-to-User access
On the User Access tab, restrict which endpoint users’ monitoring results group members can see — same mechanism as for individual users in Add a user.
7
Finish
Click Finish. The new user group appears on the Users page.
Deleting a user group doesn’t delete the users in it — but those users lose any permissions they inherited only from this group. Permissions inherited from other groups or assigned directly to the user remain.
1
Open the group
Click the Edit Group icon in the top right of the user group on the Users page.
2
Delete
On the Group Properties tab, click Delete Group at the bottom of the page.
The administrative permissions and what each one grants.
Endpoint permissions reference
The per-Endpoint permissions, plus a worked permission-inheritance example.
Which sessions a user can see
How administrative and Endpoint permissions combine to scope session access.
Two-factor authentication
Configure 2FA across users and the deployment.
ACB application accounts
Service-to-service authentication for the API.
{"docsConfig":{"theme":"mint","$schema":"https://mintlify.com/docs.json","name":"Syteca","description":"Syteca documentation - User Activity Monitoring and Privileged Access Management in a single platform.","colors":{"primary":"#2563EB","light":"#5B8DEF","dark":"#1D4ED8"},"logo":{"light":"https://mintcdn.com/syteca/ZVta4JfIcSnC47NX/logo/syteca-light.svg?fit=max\u0026auto=format\u0026n=ZVta4JfIcSnC47NX\u0026q=85\u0026s=154a18f69aa4aefa55de0de7669934c7","dark":"https://mintcdn.com/syteca/ZVta4JfIcSnC47NX/logo/syteca-dark.svg?fit=max\u0026auto=format\u0026n=ZVta4JfIcSnC47NX\u0026q=85\u0026s=07170d0c543f4264cca523f1b74b912e","href":"https://www.syteca.com/docs"},"favicon":"https://mintcdn.com/syteca/0FlD-vkHsBA1azVX/favicon.ico?fit=max\u0026auto=format\u0026n=0FlD-vkHsBA1azVX\u0026q=85\u0026s=6c6a5b9e7da5f386c9d031d55704987a","appearance":{"default":"system","strict":false},"background":{"decoration":"grid","color":{"light":"#FFFFFF","dark":"#0B0D12"}},"navbar":{"links":[{"href":"https://www.syteca.com/docs/release-notes/overview","label":"Changelog"},{"href":"https://www.syteca.com/docs/api/acb/api-reference","label":"API Reference"},{"href":"https://www.syteca.com/en/support/contact-support","label":"Support"}],"primary":{"type":"button","label":"Book a Demo","href":"https://www.syteca.com/en/book-a-demo"}},"footer":{"socials":{"youtube":"https://www.youtube.com/@syteca","linkedin":"https://www.linkedin.com/company/syteca.com"},"links":[{"header":"Product","items":[{"label":"Overview","href":"https://www.syteca.com/docs"},{"label":"Releases","href":"https://www.syteca.com/docs/release-notes/overview"},{"label":"Pricing","href":"https://syteca.com/pricing"}]},{"header":"Company","items":[{"label":"About","href":"https://www.syteca.com/en/company/about-us"}]},{"header":"Legal","items":[{"label":"Privacy","href":"https://syteca.com/privacy"},{"label":"Terms","href":"https://www.syteca.com/en/terms-of-use"}]}]},"search":{"prompt":"Syteca Documentation"},"seo":{"metatags":{"og:image":"https://www.syteca.com/og-default.png","og:site_name":"Syteca Docs","canonical":"https://www.syteca.com/docs"}},"fonts":{"heading":{"family":"Inter","weight":700},"body":{"family":"Inter","weight":400}},"icons":{"library":"lucide"},"styling":{"eyebrows":"section","codeblocks":"system","latex":false},"integrations":{"ga4":{"measurementId":"G-3SYH6XSJXQ"}},"errors":{"404":{"redirect":false}},"navigation":{"pages":[]}},"deployment":{"deploymentMetadataValue":{"subdomain":"syteca","hasAudioNarration":false,"actualSubdomain":"syteca","customDomains":["syteca.com"],"gitSource":{"type":"github","owner":"syteca","repo":"syteca-docs-poc","deployBranch":"main","contentDirectory":"","isPrivate":true,"mountPath":"","label":""},"chroma":{"liveDeploymentHistoryId":"6ae5205488bceb6cdd38a1eb","collectionId":"0a98e7ea-849b-484e-a530-a909a2a803f4","schemaVersion":"v3","latestBuiltDeploymentHistoryId":"6ae5205488bceb6cdd38a1eb"},"feedback":{"thumbs":false},"entitlements":{"AI_CHAT":{"status":"DISABLED"}},"buildId":"6ae5205488bceb6cdd38a1eb","clientVersion":"0.0.4045","searchFilterCounts":[{"language":"default","tag":"Administration","count":97},{"language":"default","tag":"API \u0026 Integrations","count":83},{"language":"default","tag":"Application Credentials Broker","count":52},{"language":"default","tag":"Session Monitoring","count":43},{"language":"default","tag":"Endpoint Risk Control","count":31},{"language":"default","tag":"Endpoints","count":29},{"language":"default","tag":"Privileged Access Management","count":26},{"language":"default","tag":"Release Notes","count":24},{"language":"default","tag":"Get Started","count":18},{"language":"default","tag":"Syteca changelog","count":18}]},"assistantConfig":{"enableAskAiButton":false,"enableStarterQuestions":false,"enableContextualStarterQuestions":false,"enableAskAiSearchBar":true},"basePath":"/docs","hasChatPermissions":false,"hasWebMcpPermissions":false,"toggles":[{"name":"kill-isr","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-mintlify-slack","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-integrations-settings","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-pr-grouping","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"custom-prefix","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"analytics-v7","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"user-flows-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"no-publish-flow","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-onboarding","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"llms-txt-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving-live","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"stripTemperatureMiddleware","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"support-platform-pylon-zendesk","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"instant-rollback","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications-server","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-fable","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fixed-ai-action-pricing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automation-resolve-merge-conflict","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"scoped-publishing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"mintql","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"page-level-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"editor-version-history-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"billing-page-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"full-page-search","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workspace-projects","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"assistant-v5","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"byok-sep-25","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fork-pr-previews","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"revalidation-jwt","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"vite-origin","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"billing-updated-9-15","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-sso-scim","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"hobby-abuse-scan","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"dashboard-inbox","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-signup","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"turbopuffer-dual-write","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-enabled","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"approve-review-flow","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"sso-setup-deadline-banner","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false}],"googleFontsInlined":false},"customCss":[{"filePath":"style.css","content":":root{--syteca-brand:#2563EB;--syteca-brand-strong:#1D4ED8;--syteca-brand-soft:#EFF6FF;--syteca-accent-green:#16A34A;--syteca-accent-amber:#D97706;--syteca-accent-violet:#7C3AED;--syteca-accent-rose:#DB2777;--syteca-accent-cyan:#0891B2;--syteca-accent-teal:#0D9488}html.dark{--syteca-brand:#5B8DEF;--syteca-brand-strong:#7AA1F3;--syteca-brand-soft:#14213D}.prose h1{letter-spacing:-.025em}.prose h2{letter-spacing:-.015em}a[class*=rounded-][class*=border]:hover{transform:translateY(-1px);transition:transform 150ms ease,box-shadow 150ms ease,border-color 150ms ease}.prose code,.prose pre{font-family:\"JetBrains Mono\",\"SF Mono\",\"Menlo\",\"Consolas\",monospace}.prose table thead th{border-bottom:2px solid var(--syteca-brand);font-weight:600}.prose table tbody td{padding-top:.55rem;padding-bottom:.55rem}figure figcaption{font-size:13px;color:rgb(113 113 122/1);margin-top:.6rem}nav[aria-label=Sidebar] a{padding-top:.3rem;padding-bottom:.3rem;font-size:13.5px}.demo-bar{display:none}"}],"page":{"pagePath":"administration/users/users","slug":"/administration/users/users","pageMetadata":{"title":"Users and User Groups","sidebarTitle":"Users","description":"Syteca user management: three user types (internal, Active Directory, application account), five default user groups, custom groups, per-Endpoint permission scoping, two-factor authentication, and admin hardening.","icon":"users","keywords":["syteca user management","rbac pam platform","active directory user groups syteca","application account acb","user-to-user access","disable default admin","syteca 2fa"],"href":"/administration/users/users"},"description":{"compiledSource":"\"use strict\";\nconst {jsx: _jsx} = arguments[0];\nconst {useMDXComponents: _provideComponents} = arguments[0];\nfunction _createMdxContent(props) {\n const _components = {\n p: \"p\",\n ..._provideComponents(),\n ...props.components\n };\n return _jsx(_components.p, {\n children: \"Syteca user management: three user types (internal, Active Directory, application account), five default user groups, custom groups, per-Endpoint permission scoping, two-factor authentication, and admin hardening.\"\n });\n}\nfunction MDXContent(props = {}) {\n const {wrapper: MDXLayout} = {\n ..._provideComponents(),\n ...props.components\n };\n return MDXLayout ? _jsx(MDXLayout, {\n ...props,\n children: _jsx(_createMdxContent, {\n ...props\n })\n }) : _createMdxContent(props);\n}\nreturn {\n default: MDXContent\n};\n","frontmatter":{},"scope":{}},"pageType":"default","mdx":{"mdxSource":{"compiledSource":"\"use strict\";const{Fragment:_Fragment,jsx:_jsx,jsxs:_jsxs}=arguments[0];const{useMDXComponents:_provideComponents}=arguments[0];function _createMdxContent(props){const _components={a:`a`,code:`code`,em:`em`,li:`li`,p:`p`,strong:`strong`,tbody:`tbody`,td:`td`,th:`th`,thead:`thead`,tr:`tr`,ul:`ul`,..._provideComponents(),...props.components},{Card,CardGroup,Frame,Heading,Info,Note,OptimizedImage,Step,Steps,Tab,Table,Tabs,Tip,Warning}=_components;if(!Card)_missingMdxReference(`Card`,true);if(!CardGroup)_missingMdxReference(`CardGroup`,true);if(!Frame)_missingMdxReference(`Frame`,true);if(!Heading)_missingMdxReference(`Heading`,true);if(!Info)_missingMdxReference(`Info`,true);if(!Note)_missingMdxReference(`Note`,true);if(!OptimizedImage)_missingMdxReference(`OptimizedImage`,true);if(!Step)_missingMdxReference(`Step`,true);if(!Steps)_missingMdxReference(`Steps`,true);if(!Tab)_missingMdxReference(`Tab`,true);if(!Table)_missingMdxReference(`Table`,true);if(!Tabs)_missingMdxReference(`Tabs`,true);if(!Tip)_missingMdxReference(`Tip`,true);if(!Warning)_missingMdxReference(`Warning`,true);return _jsxs(_Fragment,{children:[_jsx(Heading,{level:`2`,id:`rbac-built-for-the-people-who-run-a-pam-platform`,children:`RBAC built for the people who run a PAM platform`}),`\n`,_jsxs(_components.p,{children:[`Every security platform has user roles. Most do the minimum: admin, operator, viewer, maybe a custom role tier and call it RBAC. That works until you’re running a real PAM and User Activity Monitoring deployment, at which point you need to express things like: `,_jsx(_components.em,{children:`“Sarah can view monitoring results for the Finance Endpoint group but not Engineering, can’t see clipboard text, can approve One-Time Password requests, can’t disable the default admin, and her permissions inherit from the Supervisors user group except when overridden by her own grants.”`}),` Generic RBAC doesn’t fit that shape; you either over-grant and hope, or you write workarounds.`]}),`\n`,_jsxs(_components.p,{children:[`Competitors at this layer handle similar problems with their own permission models, but with varying granularity. `,_jsx(_components.strong,{children:`Syteca’s permission model`}),` is built around exactly the operations a UAM/PAM admin needs: `,_jsx(_components.a,{href:`/administration/users/administrative-permissions`,children:`administrative permissions`}),` that gate platform-wide actions, `,_jsx(_components.a,{href:`/administration/users/client-permissions`,children:`Endpoint permissions`}),` that gate per-Endpoint operations, `,_jsx(_components.strong,{children:`User-to-User access scoping`}),` for restricting which `,_jsx(_components.em,{children:`endpoint users’`}),` monitoring results a Management Tool user can see, and three user types (internal, Active Directory, application account) that share the same permission engine.`]}),`\n`,_jsxs(Info,{children:[_jsx(_components.p,{children:_jsx(_components.strong,{children:`Use Syteca user management when you need to:`})}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`Implement `,_jsx(_components.strong,{children:`separation of duties`}),` between platform admins, investigators, and operations staff — with permissions granular enough to express the real boundaries.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Inherit AD user groups`}),` automatically — domain group → Management Tool user group → user, so new hires get correct access on day one.`]}),`\n`,_jsxs(_components.li,{children:[`Restrict `,_jsx(_components.strong,{children:`which endpoint users a given investigator can monitor`}),` (the “User-to-User” model) — useful for legal-team segmentation, regional separation, or contractor isolation.`]}),`\n`,_jsxs(_components.li,{children:[`Scope an investigator to `,_jsx(_components.strong,{children:`only the sessions where an alert fired`}),`, so granting access to one incident doesn’t grant access to everything else recorded on that endpoint — see `,_jsx(_components.a,{href:`/administration/users/session-visibility`,children:`Which sessions a user can see`}),`.`]}),`\n`,_jsxs(_components.li,{children:[`Enforce `,_jsx(_components.strong,{children:`2FA per user`}),` — TOTP via any authenticator app — with admin-managed reset for lost devices.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Harden the default admin`}),` by disabling it entirely once other Administrators are configured — eliminates the “default admin compromise” attack surface.`]}),`\n`,_jsxs(_components.li,{children:[`Wire applications into Syteca via `,_jsx(_components.strong,{children:`Application Account users`}),` through the `,_jsx(_components.a,{href:`/api/acb/overview`,children:`Application Credentials Broker`}),` for service-to-service automation.`]}),`\n`]}),_jsxs(_components.p,{children:[_jsxs(_components.strong,{children:[`Pair it with `,_jsx(_components.a,{href:`/administration/access/smart-card-access`,children:`Smart card access`})]}),` — RBAC scopes `,_jsx(_components.em,{children:`what`}),` a user can do; smart card access scopes `,_jsx(_components.em,{children:`who can authenticate as that user`}),`. Defense in depth.`]})]}),`\n`,_jsx(Note,{children:_jsxs(_components.p,{children:[`All user and user group management requires the `,_jsx(_components.a,{href:`/administration/users/administrative-permissions`,children:`administrative User Management permission`}),`. In Multi-Tenant mode, users and user groups are completely independent per tenant.`]})}),`\n`,_jsx(Heading,{level:`2`,id:`the-default-admin-and-tenant-model`,children:`The default admin and tenant model`}),`\n`,_jsxs(_components.p,{children:[`By default, Syteca ships with one administrator — login `,_jsx(_components.code,{children:`admin`}),`, password set during `,_jsx(_components.a,{href:`/administration/deployment/install-application-server`,children:`Application Server installation`}),`. The default admin has every permission required to work with the system and is the `,_jsx(_components.strong,{children:`technician`}),` in Multi-Tenant mode, with the ability to create tenants. Once another admin is configured, `,_jsx(_components.a,{href:`#disable-the-default-admin`,children:`the default admin can be disabled`}),` to harden the deployment.`]}),`\n`,_jsx(Heading,{level:`2`,id:`three-user-types`,children:`Three user types`}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`User type`}),_jsx(_components.th,{children:`Best for`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Internal`})}),_jsx(_components.td,{children:`Local Management Tool accounts are most common for small deployments or for break-glass admin accounts. Authenticate with username + password defined in Syteca.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Active Directory`})}),_jsxs(_components.td,{children:[`Domain users and domain user groups are most common for enterprise deployments. Authenticate with AD credentials. Requires an `,_jsx(_components.a,{href:`/administration/integrations/ldap-targets`,children:`LDAP target`}),` configured.`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Application Account`})}),_jsxs(_components.td,{children:[`Service-to-service accounts for the `,_jsx(_components.a,{href:`/api/acb/overview`,children:`Application Credentials Broker (ACB)`}),` API. Authenticate with a `,_jsx(_components.a,{href:`/api/acb/setup-user-account`,children:`Client ID and Client Secret`}),`. `,_jsx(_components.strong,{children:`Not available in SaaS.`})]})]})]})]}),`\n`,_jsx(Heading,{level:`2`,id:`five-default-user-groups`,children:`Five default user groups`}),`\n`,_jsx(_components.p,{children:`Every Syteca deployment ships with four user groups:`}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Group`}),_jsx(_components.th,{children:`Contains`}),_jsx(_components.th,{children:`Permissions`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`All Users`})}),_jsx(_components.td,{children:`Every user — automatic, can’t be removed`}),_jsx(_components.td,{children:`None inherent`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Administrators`})}),_jsx(_components.td,{children:`Users who can perform administrative functions`}),_jsxs(_components.td,{children:[_jsx(_components.strong,{children:`All`}),` administrative and Endpoint permissions`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Supervisors`})}),_jsx(_components.td,{children:`Users whose job is to analyze Endpoints`}),_jsxs(_components.td,{children:[_jsx(_components.strong,{children:`Viewing All Monitoring Results`}),` for all Endpoints`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`PAM Users`})}),_jsxs(_components.td,{children:[`Users of `,_jsx(_components.a,{href:`/pam/access/desktop-connection-manager`,children:`Syteca Connection Manager`}),` who don’t have Management Tool access`]}),_jsx(_components.td,{children:`None for Management Tool`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Application Accounts`})}),_jsxs(_components.td,{children:[`Service-to-service accounts for the `,_jsx(_components.a,{href:`/api/acb/overview`,children:`Application Credentials Broker (ACB)`}),` API. Authenticate with a `,_jsx(_components.a,{href:`/api/acb/setup-user-account`,children:`Client ID and Client Secret`})]}),_jsx(_components.td,{children:`None for Management Tool`})]})]})]}),`\n`,_jsx(Warning,{children:_jsxs(_components.p,{children:[`The default `,_jsx(_components.code,{children:`admin`}),` user of the built-in default tenant `,_jsx(_components.strong,{children:`cannot be removed`}),` from the `,_jsx(_components.strong,{children:`Administrators`}),` user group.`]})}),`\n`,_jsxs(_components.p,{children:[`You can add custom user groups for finer-grained role definitions — see `,_jsx(_components.a,{href:`#add-a-user-group`,children:`Add a user group`}),` below.`]}),`\n`,_jsx(Heading,{level:`2`,id:`permission-inheritance`,children:`Permission inheritance`}),`\n`,_jsx(_components.p,{children:`A user can belong to multiple user groups. When a user is in a group:`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`They `,_jsx(_components.strong,{children:`inherit`}),` every permission granted to that group.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Inherited permissions can only be removed by removing the user from the group`}),` they can’t be revoked individually on the user.`]}),`\n`,_jsxs(_components.li,{children:[`The user can also have `,_jsx(_components.strong,{children:`their own`}),` permissions in addition to inherited ones.`]}),`\n`]}),`\n`,_jsxs(_components.p,{children:[`If an Active Directory user is added as an independent internal user `,_jsx(_components.strong,{children:`and`}),` as a member of a Windows domain user group, `,_jsx(_components.strong,{children:`the user’s own permissions take priority`}),` over the domain-group-inherited ones.`]}),`\n`,_jsxs(_components.p,{children:[`For a worked example of how user-level and group-level permissions combine, see `,_jsx(_components.a,{href:`/administration/users/client-permissions#example-of-permission-inheritance`,children:`Example of permissions`}),`.`]}),`\n`,_jsx(Heading,{level:`2`,id:`open-the-users-page`,children:`Open the Users page`}),`\n`,_jsxs(_components.p,{children:[`Sign in to the Management Tool, click `,_jsx(_components.strong,{children:`Users`}),` in the left navigation. Users are listed grouped by the user groups they belong to. Each row shows:`]}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Column`}),_jsx(_components.th,{children:`Shows`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Login`})}),_jsx(_components.td,{children:`The user’s login name.`})]}),_jsxs(_components.tr,{children:[_jsxs(_components.td,{children:[_jsx(_components.strong,{children:`First Name`}),` / `,_jsx(_components.strong,{children:`Last Name`})]}),_jsxs(_components.td,{children:[`Filled in manually for internal users; `,_jsx(_components.strong,{children:`auto-populated for AD users after first sign-in`}),`.`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Description`})}),_jsx(_components.td,{children:`Optional description.`})]}),_jsxs(_components.tr,{children:[_jsxs(_components.td,{children:[_jsx(_components.strong,{children:`PAM`}),` `,_jsx(_components.em,{children:`(toggle)`})]}),_jsxs(_components.td,{children:[`Whether the user has a `,_jsx(_components.a,{href:`/administration/licensing/assign-pam-seat-licenses`,children:`PAM seat license`}),` assigned — required for Password Management and Account Discovery.`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Status`})}),_jsxs(_components.td,{children:[_jsx(_components.strong,{children:`Active`}),` or `,_jsx(_components.strong,{children:`Locked`}),`, plus icons for `,_jsx(_components.strong,{children:`Edit User`}),` and `,_jsx(_components.strong,{children:`Lock User`}),` / `,_jsx(_components.strong,{children:`Unlock User`}),`.`]})]})]})]}),`\n`,_jsx(Tip,{children:_jsxs(_components.p,{children:[`Use the `,_jsx(_components.strong,{children:`Search box`}),` at the top to find users or user groups by user name, group name, first name, last name, or description.`]})}),`\n`,_jsx(Frame,{caption:`The Users page - users listed under the groups they belong to, with PAM seat toggle and lock/unlock status visible per row.`,children:_jsx(OptimizedImage,{src:`https://mintcdn.com/syteca/FKrkO8bEqEQ6WSgs/images/administration/users/users-page-grid.png?fit=max\u0026auto=format\u0026n=FKrkO8bEqEQ6WSgs\u0026q=85\u0026s=833544f2eb9c57eeeca9a61808eb190c`,alt:`Users page showing the user list grouped by user groups with Login, names, Description, PAM toggle, and Status columns`,\"data-og-width\":`1913`,width:`1913`,\"data-og-height\":`696`,height:`696`,\"data-path\":`images/administration/users/users-page-grid.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/syteca/FKrkO8bEqEQ6WSgs/images/administration/users/users-page-grid.png?w=280\u0026fit=max\u0026auto=format\u0026n=FKrkO8bEqEQ6WSgs\u0026q=85\u0026s=a2ed2c55c25bf709a7411b81919ec979 280w, https://mintcdn.com/syteca/FKrkO8bEqEQ6WSgs/images/administration/users/users-page-grid.png?w=560\u0026fit=max\u0026auto=format\u0026n=FKrkO8bEqEQ6WSgs\u0026q=85\u0026s=9832fc4f42ed69c13d2be62216f74e20 560w, https://mintcdn.com/syteca/FKrkO8bEqEQ6WSgs/images/administration/users/users-page-grid.png?w=840\u0026fit=max\u0026auto=format\u0026n=FKrkO8bEqEQ6WSgs\u0026q=85\u0026s=f579f62dc147e752accbe0703ee50ee5 840w, https://mintcdn.com/syteca/FKrkO8bEqEQ6WSgs/images/administration/users/users-page-grid.png?w=1100\u0026fit=max\u0026auto=format\u0026n=FKrkO8bEqEQ6WSgs\u0026q=85\u0026s=5b4ef45ec701e08c3e0acabacb3f69b2 1100w, https://mintcdn.com/syteca/FKrkO8bEqEQ6WSgs/images/administration/users/users-page-grid.png?w=1650\u0026fit=max\u0026auto=format\u0026n=FKrkO8bEqEQ6WSgs\u0026q=85\u0026s=c857cc3831d253a56ae96dff14214b77 1650w, https://mintcdn.com/syteca/FKrkO8bEqEQ6WSgs/images/administration/users/users-page-grid.png?w=2500\u0026fit=max\u0026auto=format\u0026n=FKrkO8bEqEQ6WSgs\u0026q=85\u0026s=7aedffe060d80e8426edc0621f700000 2500w`})}),`\n`,_jsx(Heading,{level:`2`,id:`add-a-user`,children:`Add a user`}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`Open Add User`,children:_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`Users`}),` page, click `,_jsx(_components.strong,{children:`Add User`}),` in the top right.`]})}),_jsxs(Step,{title:`Pick the user type`,children:[_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`User Type`}),` tab of the `,_jsx(_components.strong,{children:`Adding New User`}),` page, click one:`]}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Add an Internal User`}),` will create a local Management Tool account.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Add an Active Directory User / User Group`}),` will add an existing AD user or user group.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Add Application Account`}),` will create an account for the `,_jsx(_components.a,{href:`/api/acb/overview`,children:`ACB API`}),`. `,_jsx(_components.em,{children:`Not available in SaaS.`})]}),`\n`]}),_jsx(Warning,{children:_jsxs(_components.p,{children:[`Active Directory users / user groups can’t be added if no `,_jsx(_components.a,{href:`/administration/integrations/ldap-targets`,children:`LDAP target`}),` has been configured for the domain, or if the domain is currently unavailable.`]})}),_jsx(Note,{children:_jsx(_components.p,{children:`If an Active Directory user already belongs to two or more AD user groups in Syteca, that user can’t add themselves as an independent user — only other administrators with appropriate permissions can.`})})]}),_jsxs(Step,{title:`Fill in user details`,children:[_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`User Details`}),` tab, complete the form depending on user type:`]}),_jsxs(Tabs,{children:[_jsx(Tab,{title:`Internal user`,id:`internal-user`,children:_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Login`}),` must be unique. `,_jsx(_components.em,{children:`(In Multi-Tenant mode, users of different tenants can share the same login.)`})]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Password`}),` at least 8 characters, with at least one lowercase letter, one uppercase letter, one numeric character, and one special character. Cannot contain more than 3 consecutive identical characters or the user’s login name.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`First Name`}),` / `,_jsx(_components.strong,{children:`Last Name`}),` / `,_jsx(_components.strong,{children:`Description`}),` optional, max 200 characters each.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Email`}),` is required for the user to receive an automatically generated one-time password.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Enable two-factor authentication on login`}),` force the user to set up TOTP 2FA on first sign-in.`]}),`\n`]})}),_jsx(Tab,{title:`Active Directory user/group`,id:`active-directory-user%2Fgroup`,children:_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`User / User Group`}),` will search across any configured domain and select.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Enable two-factor authentication on login`}),` force 2FA in addition to AD authentication.`]}),`\n`]})}),_jsx(Tab,{title:`Application Account`,id:`application-account`,children:_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Login`}),` — name of the application account.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Client ID / Client Secret authentication`}),` — the Client ID is generated automatically and can’t be edited. Add one or more Client Secrets for the applications that will call the API.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Refresh Token-Based Authentication`}),` — legacy, and deprecated from 7.28. See `,_jsx(_components.a,{href:`/api/acb/setup-user-account`,children:`Set up a user account`}),` for both, and `,_jsx(_components.a,{href:`/api/acb/migrate-to-client-credentials`,children:`Migrate to Client ID / Client Secret`}),` for the transition.`]}),`\n`]})})]}),_jsx(Note,{children:_jsxs(_components.p,{children:[`Internal and Active Directory users can also call the ACB API. Enable `,_jsx(_components.strong,{children:`Allow this user account to be used by external applications`}),` in the `,_jsx(_components.strong,{children:`Application Account Settings`}),` section of this tab, and the same Client ID / Client Secret and Refresh Token sections appear. See `,_jsx(_components.a,{href:`/api/acb/setup-user-account`,children:`Set up a user account`}),`.`]})}),_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Next`}),`.`]})]}),_jsxs(Step,{title:`Assign user groups`,children:[_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`User Groups`}),` tab, select the groups this user will belong to. Click `,_jsx(_components.strong,{children:`Next`}),`.`]}),_jsx(Note,{children:_jsxs(_components.p,{children:[`The user is automatically added to the `,_jsx(_components.strong,{children:`All Users`}),` default group — this can’t be changed.`]})})]}),_jsxs(Step,{title:`Set administrative permissions`,children:[_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`Administrative Permissions`}),` tab, select the `,_jsx(_components.a,{href:`/administration/users/administrative-permissions`,children:`administrative permissions`}),` to grant the user directly (in addition to any inherited from groups).`]}),_jsx(Note,{children:_jsxs(_components.p,{children:[`You can only `,_jsx(_components.strong,{children:`add`}),` new permissions on top of group-inherited ones. To remove inherited permissions, remove the user from the relevant group.`]})}),_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Next`}),`.`]})]}),_jsxs(Step,{title:`Set Endpoint access`,children:[_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`Endpoint Access`}),` tab, for each Endpoint or Endpoint group:`]}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`Click the `,_jsx(_components.strong,{children:`Edit Permissions`}),` icon on the right.`]}),`\n`,_jsxs(_components.li,{children:[`In the `,_jsx(_components.strong,{children:`Endpoint Permissions`}),` window, select which `,_jsx(_components.a,{href:`/administration/users/client-permissions`,children:`Endpoint permissions`}),` to grant.`]}),`\n`,_jsxs(_components.li,{children:[`Click `,_jsx(_components.strong,{children:`Save`}),`.`]}),`\n`]}),_jsx(Note,{children:_jsxs(_components.p,{children:[`Two of these permissions decide which sessions the user can see: `,_jsx(_components.strong,{children:`Viewing All Monitoring Results`}),` reveals every session on the Endpoint, and `,_jsx(_components.strong,{children:`Viewing Alerted Sessions`}),` reveals only those containing a triggered alert. Neither lets the user open a session on its own. See `,_jsx(_components.a,{href:`/administration/users/session-visibility`,children:`Which sessions a user can see`}),`.`]})}),_jsx(Tip,{children:_jsxs(_components.p,{children:[`Use the `,_jsx(_components.strong,{children:`Search box`}),` + `,_jsx(_components.strong,{children:`Apply Filters`}),` button at the top to find specific Endpoints or groups by name.`]})}),_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Next`}),`.`]})]}),_jsxs(Step,{title:`(Optional) Set User-to-User access`,children:[_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`User Access`}),` tab, restrict `,_jsx(_components.em,{children:`which endpoint users’ monitoring results this Management Tool user can see`}),`. If you leave this empty, the user sees sessions for all endpoint users they have Viewing Monitoring Results permission for.`]}),_jsx(_components.p,{children:`To restrict:`}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`Click `,_jsx(_components.strong,{children:`Add User`}),` on the right.`]}),`\n`,_jsxs(_components.li,{children:[`Pick the `,_jsx(_components.strong,{children:`Domain / Computer Name`}),` and `,_jsx(_components.strong,{children:`User / User Group`}),` from the drop-downs. `,_jsxs(_components.strong,{children:[`Use `,_jsx(_components.code,{children:`*`}),` as a wildcard.`]})]}),`\n`,_jsxs(_components.li,{children:[`Click the `,_jsx(_components.strong,{children:`Add`}),` icon to commit.`]}),`\n`]}),_jsx(Note,{children:_jsx(_components.p,{children:`The drop-downs only show domains, computers, users, and groups already seen by Syteca during monitoring — but you can also type new names directly.`})}),_jsx(Note,{children:_jsxs(_components.p,{children:[`Settings here apply to `,_jsx(_components.strong,{children:`all`}),` sessions for the added endpoint users — past and future. `,_jsx(_components.strong,{children:`Exception:`}),` if you add a `,_jsx(_components.em,{children:`domain group`}),`, only sessions recorded `,_jsx(_components.em,{children:`after`}),` adding the group are accessible.`]})})]}),_jsx(Step,{title:`(Optional) Assign a PAM seat license`,children:_jsxs(_components.p,{children:[`After saving, on the `,_jsx(_components.strong,{children:`Users`}),` page, toggle the `,_jsx(_components.strong,{children:`PAM`}),` column on for users who need `,_jsx(_components.a,{href:`/pam/overview`,children:`Password Management`}),` and `,_jsx(_components.a,{href:`/pam/discovery/overview`,children:`Account Discovery`}),` — see `,_jsx(_components.a,{href:`/administration/licensing/assign-pam-seat-licenses`,children:`PAM seat licenses`}),`.`]})}),_jsx(Step,{title:`Finish`,children:_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Finish`}),` in the bottom right. The new user appears on the Users page.`]})})]}),`\n`,_jsx(Heading,{level:`2`,id:`edit-a-user`,children:`Edit a user`}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`Open the user`,children:_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`Users`}),` page, click the `,_jsx(_components.strong,{children:`Edit User`}),` icon next to the user.`]})}),_jsx(Step,{title:`Make your changes`,children:_jsxs(_components.p,{children:[`Edit the user details, group memberships, permissions, Endpoint access, and User-to-User access on the corresponding tabs — same as when `,_jsx(_components.a,{href:`#add-a-user`,children:`adding a user`}),`.`]})}),_jsx(Step,{title:`Reset 2FA (if needed)`,children:_jsxs(_components.p,{children:[`A `,_jsx(_components.strong,{children:`Reset 2FA`}),` button appears next to the `,_jsx(_components.strong,{children:`Enable two-factor authentication on login`}),` checkbox — but `,_jsx(_components.strong,{children:`only after`}),` the user has already signed in and set up 2FA, and `,_jsx(_components.strong,{children:`only for`}),` the tenant admin and Management Tool users with the User Management permission. Click it to delete the user’s 2FA profile, useful when the user has lost both their phone and their 2FA recovery code.`]})}),_jsx(Step,{title:`Save`,children:_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Finish`}),` to save and exit, or `,_jsx(_components.strong,{children:`Next`}),` to save progressively across tabs.`]})})]}),`\n`,_jsx(Note,{children:_jsxs(_components.p,{children:[`The `,_jsx(_components.strong,{children:`Delete User`}),` button appears in the bottom left when editing — see `,_jsx(_components.a,{href:`#delete-a-user`,children:`Delete a user`}),` below. For the default `,_jsx(_components.code,{children:`admin`}),` user, the `,_jsx(_components.strong,{children:`Disable User`}),` button replaces `,_jsx(_components.strong,{children:`Delete User`}),` — see `,_jsx(_components.a,{href:`#disable-the-default-admin`,children:`Disable the default admin`}),`.`]})}),`\n`,_jsx(Heading,{level:`2`,id:`lock-and-unlock-users`,children:`Lock and unlock users`}),`\n`,_jsxs(_components.p,{children:[`User accounts can be locked automatically (after too many failed sign-ins — see `,_jsx(_components.a,{href:`/get-started/management-tool-basics#lock-user-accounts-on-multiple-failed-sign-in-attempts`,children:`Brute-force lockout`}),`) or manually by an administrator.`]}),`\n`,_jsxs(Tabs,{children:[_jsx(Tab,{title:`Lock a user`,id:`lock-a-user`,children:_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`Users`}),` page, click the `,_jsx(_components.strong,{children:`Lock User`}),` icon on the right of the user. Click `,_jsx(_components.strong,{children:`Confirm`}),` in the pop-up.`]})}),_jsx(Tab,{title:`Unlock a user`,id:`unlock-a-user`,children:_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`Users`}),` page, click the `,_jsx(_components.strong,{children:`Unlock User`}),` icon. Click `,_jsx(_components.strong,{children:`Confirm`}),` in the pop-up.`]})})]}),`\n`,_jsx(Heading,{level:`2`,id:`delete-a-user`,children:`Delete a user`}),`\n`,_jsx(Warning,{children:_jsx(_components.p,{children:`Deleting a user means they immediately lose access to the system. If they’re signed in at the moment of deletion, the Management Tool becomes unavailable immediately and pages stop loading.`})}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`Open the user`,children:_jsxs(_components.p,{children:[`Click the `,_jsx(_components.strong,{children:`Edit User`}),` icon next to the user on the Users page.`]})}),_jsx(Step,{title:`Delete`,children:_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`User Details`}),` tab, click `,_jsx(_components.strong,{children:`Delete User`}),` in the bottom left.`]})}),_jsx(Step,{title:`Confirm`,children:_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Delete`}),` in the confirmation message.`]})})]}),`\n`,_jsx(Note,{children:_jsxs(_components.p,{children:[`The default `,_jsx(_components.code,{children:`admin`}),` user can’t be deleted — use `,_jsx(_components.a,{href:`#disable-the-default-admin`,children:`Disable the default admin`}),` instead.`]})}),`\n`,_jsx(Heading,{level:`2`,id:`disable-the-default-admin`,children:`Disable the default admin`}),`\n`,_jsxs(_components.p,{children:[`The default `,_jsx(_components.code,{children:`admin`}),` user has unrestricted access to everything in Syteca — useful for initial setup, a meaningful risk during operation. After initial deployment, security-conscious organizations disable the default admin entirely and rely on other Administrators users (each with auditable, configurable permissions) to operate the platform.`]}),`\n`,_jsx(Frame,{caption:`On the default admin user's Edit page, the Disable User button replaces the Delete User button - and only appears when another Administrators-group user exists.`,children:_jsx(OptimizedImage,{src:`https://mintcdn.com/syteca/FKrkO8bEqEQ6WSgs/images/administration/users/disable-default-admin-button.png?fit=max\u0026auto=format\u0026n=FKrkO8bEqEQ6WSgs\u0026q=85\u0026s=e830bdf220ebea1524ed8fa044a03b7f`,alt:`Edit User page for the default admin showing the Disable User button in the bottom left replacing the Delete User button`,\"data-og-width\":`1144`,width:`1144`,\"data-og-height\":`984`,height:`984`,\"data-path\":`images/administration/users/disable-default-admin-button.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/syteca/FKrkO8bEqEQ6WSgs/images/administration/users/disable-default-admin-button.png?w=280\u0026fit=max\u0026auto=format\u0026n=FKrkO8bEqEQ6WSgs\u0026q=85\u0026s=ead393fc1001880969cc873943bb2991 280w, https://mintcdn.com/syteca/FKrkO8bEqEQ6WSgs/images/administration/users/disable-default-admin-button.png?w=560\u0026fit=max\u0026auto=format\u0026n=FKrkO8bEqEQ6WSgs\u0026q=85\u0026s=0df899fbdd1148083f8cee93c31a8a99 560w, https://mintcdn.com/syteca/FKrkO8bEqEQ6WSgs/images/administration/users/disable-default-admin-button.png?w=840\u0026fit=max\u0026auto=format\u0026n=FKrkO8bEqEQ6WSgs\u0026q=85\u0026s=4404aae99f9e48e84fd27a8e58ba3cdd 840w, https://mintcdn.com/syteca/FKrkO8bEqEQ6WSgs/images/administration/users/disable-default-admin-button.png?w=1100\u0026fit=max\u0026auto=format\u0026n=FKrkO8bEqEQ6WSgs\u0026q=85\u0026s=1561956af109cfce240f1127202d6ae4 1100w, https://mintcdn.com/syteca/FKrkO8bEqEQ6WSgs/images/administration/users/disable-default-admin-button.png?w=1650\u0026fit=max\u0026auto=format\u0026n=FKrkO8bEqEQ6WSgs\u0026q=85\u0026s=275f265a2174a54d2c2c931454511de5 1650w, https://mintcdn.com/syteca/FKrkO8bEqEQ6WSgs/images/administration/users/disable-default-admin-button.png?w=2500\u0026fit=max\u0026auto=format\u0026n=FKrkO8bEqEQ6WSgs\u0026q=85\u0026s=0f95438e2dbdc9bb0c7cb0d2e1dfcefe 2500w`})}),`\n`,_jsxs(Info,{children:[_jsx(_components.p,{children:_jsx(_components.strong,{children:`Why disable the default admin?`})}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`Eliminates a known, high-value credential target (the literal `,_jsx(_components.code,{children:`admin`}),` account).`]}),`\n`,_jsxs(_components.li,{children:[`Forces all administrative actions through accounts that show up in the `,_jsx(_components.a,{href:`/administration/audit-log`,children:`Audit log`}),` by name.`]}),`\n`,_jsx(_components.li,{children:`Meets compliance frameworks (NIST 800-53 IA-4, ISO 27001 A.9.2) that restrict generic admin accounts.`}),`\n`,_jsx(_components.li,{children:`Required by some Pseudonymizer / regulatory deployment patterns.`}),`\n`]})]}),`\n`,_jsx(Heading,{level:`3`,id:`prerequisites`,children:`Prerequisites`}),`\n`,_jsxs(_components.p,{children:[`Before disabling the default admin, `,_jsx(_components.strong,{children:`at least one other user must be added to the Administrators user group`}),` — either as an internal user, an AD user, or via membership in an AD user group added to Administrators.`]}),`\n`,_jsxs(_components.p,{children:[`Additionally, the default admin can’t be disabled while they’re the `,_jsx(_components.strong,{children:`sole owner`}),` of certain options or rules. Address these first:`]}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Option / Rule`}),_jsx(_components.th,{children:`Block`}),_jsx(_components.th,{children:`Remediation`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Scheduled Reports`})}),_jsxs(_components.td,{children:[`Default admin is the only user in `,_jsx(_components.strong,{children:`Who Can Download`}),` for a `,_jsx(_components.a,{href:`/session-monitoring/reports/scheduled-reports`,children:`Scheduled Report rule`}),`.`]}),_jsxs(_components.td,{children:[`Add another user to the `,_jsx(_components.strong,{children:`Who Can Download`}),` field.`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Secrets`})}),_jsxs(_components.td,{children:[`Default admin is the only `,_jsx(_components.strong,{children:`Owner`}),` of a `,_jsx(_components.a,{href:`/pam/secrets/view-manage-secrets`,children:`secret`}),`.`]}),_jsx(_components.td,{children:`Add another user as Owner of the secret.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Folders`})}),_jsxs(_components.td,{children:[`Default admin is the only `,_jsx(_components.strong,{children:`Owner`}),` of a folder (including `,_jsx(_components.a,{href:`/pam/secrets/workforce-password-management`,children:`Workforce Password Management`}),` folders).`]}),_jsx(_components.td,{children:`Add another user as Owner of the folder.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Endpoint Access requests`})}),_jsxs(_components.td,{children:[`Default admin is the only user who can approve `,_jsx(_components.a,{href:`/administration/access/endpoint-access-control`,children:`Endpoint Access`}),` requests.`]}),_jsxs(_components.td,{children:[`Add another user to `,_jsx(_components.strong,{children:`Users Who Can Approve Access`}),`.`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`One-Time Password requests`})}),_jsxs(_components.td,{children:[`Default admin is the only user who can approve `,_jsx(_components.a,{href:`/pam/secrets/password-checkout`,children:`OTP requests`}),`.`]}),_jsxs(_components.td,{children:[`Add another user to `,_jsx(_components.strong,{children:`Users who can approve access`}),` on the `,_jsx(_components.strong,{children:`Authentication Options`}),` tab of Editing Endpoint / Endpoint Group.`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Access to Usage of Secret`})}),_jsxs(_components.td,{children:[`Default admin is the only user who can approve `,_jsx(_components.a,{href:`/pam/secrets/use-secrets`,children:`secret-usage requests`}),`.`]}),_jsxs(_components.td,{children:[`Add another user to `,_jsx(_components.strong,{children:`Users who can approve access`}),` on the `,_jsx(_components.strong,{children:`Restrictions`}),` tab of Edit Secret.`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Mass Storage Device Access`})}),_jsxs(_components.td,{children:[`Default admin is the only user who can approve `,_jsx(_components.a,{href:`/session-monitoring/usb-devices/usb-access-approval`,children:`USB access requests`}),`.`]}),_jsxs(_components.td,{children:[`Add another user to `,_jsx(_components.strong,{children:`Users who can approve access`}),` on the `,_jsx(_components.strong,{children:`Additional Options`}),` tab of the USB rule.`]})]})]})]}),`\n`,_jsx(Note,{children:_jsxs(_components.p,{children:[`If the default admin is the `,_jsx(_components.strong,{children:`owner`}),` (i.e. created) of a Scheduled Report rule, disabling the default admin `,_jsx(_components.strong,{children:`stops the rule from running`}),` and removes it from the Scheduled Reports tab. To preserve the rule, transfer ownership before disabling — or recreate the rule under another user.`]})}),`\n`,_jsx(Heading,{level:`3`,id:`disable-the-default-admin-2`,children:`Disable the default admin`}),`\n`,_jsxs(Steps,{children:[_jsxs(Step,{title:`Sign in as another administrator`,children:[_jsxs(_components.p,{children:[`Sign in to the Management Tool as `,_jsx(_components.strong,{children:`any user in the Administrators group except the default admin`}),`.`]}),_jsx(Note,{children:_jsxs(_components.p,{children:[`Only users in the default `,_jsx(_components.strong,{children:`Administrators`}),` user group (internal or AD, or AD user-group members) can disable the default admin.`]})})]}),_jsx(Step,{title:`Open the default admin`,children:_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Users`}),` in the left navigation. Click the `,_jsx(_components.strong,{children:`Edit User`}),` icon next to the default `,_jsx(_components.code,{children:`admin`}),` user.`]})}),_jsxs(Step,{title:`Click Disable User`,children:[_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`User Details`}),` tab, click `,_jsx(_components.strong,{children:`Disable User`}),` in the bottom left.`]}),_jsx(Note,{children:_jsxs(_components.p,{children:[`The `,_jsx(_components.strong,{children:`Disable User`}),` button replaces `,_jsx(_components.strong,{children:`Delete User`}),` for the default admin. It only appears if at least one other user has been added to the Administrators group.`]})})]}),_jsx(Step,{title:`Confirm`,children:_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Confirm`}),` in the warning pop-up. If the default admin is the sole owner of any options/rules listed in the prerequisites table, the `,_jsx(_components.strong,{children:`Confirm`}),` button won’t be available — resolve those first.`]})})]}),`\n`,_jsxs(_components.p,{children:[`After the default admin is disabled, `,_jsx(_components.strong,{children:`the last remaining user in the Administrators group cannot be deleted`}),` — Syteca preserves at least one administrator.`]}),`\n`,_jsx(Heading,{level:`3`,id:`restrictions-after-disabling`,children:`Restrictions after disabling`}),`\n`,_jsx(_components.p,{children:`Disabling the default admin changes the behavior of several features:`}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Feature`}),_jsx(_components.th,{children:`Behavior after disabling`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:_jsx(_components.a,{href:`/session-monitoring/masking/pseudonymizer`,children:`Pseudonymizer`})})}),_jsxs(_components.td,{children:[`The `,_jsx(_components.strong,{children:`Enable De-Anonymization Password`}),` section is hidden on the Pseudonymization configuration tab. If the password was set before disabling, `,_jsx(_components.strong,{children:`it continues to function`}),` but `,_jsx(_components.strong,{children:`cannot be deselected or changed`}),` until the default admin is re-enabled.`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:_jsx(_components.a,{href:`/api/data-connector/overview`,children:`Syteca API Data Connector`})})}),_jsxs(_components.td,{children:[`The default admin’s API key can no longer be used for API requests. Use the API key of any Administrators-group user instead. `,_jsx(_components.strong,{children:`Note:`}),` Data Connector v.1.9 installation still requires the default admin credentials, so install before disabling.`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:_jsx(_components.a,{href:`/pam/discovery/overview`,children:`Account Discovery`})})}),_jsxs(_components.td,{children:[`If the default admin was in the `,_jsx(_components.strong,{children:`Send email notifications about new accounts found to`}),` field of an Account Discovery rule, they’re removed from it and no longer receive notifications.`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:_jsx(_components.a,{href:`/administration/multi-tenant/overview`,children:`Multi-Tenant mode`})})}),_jsxs(_components.td,{children:[`The default `,_jsx(_components.code,{children:`admin`}),` username no longer appears in the `,_jsx(_components.strong,{children:`Tenant Admin`}),` column for the Built-in default tenant on the Tenants page.`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:_jsx(_components.a,{href:`/administration/deployment/high-availability`,children:`High Availability mode`})})}),_jsx(_components.td,{children:`Installing Syteca Application Server in High Availability (including with load balancing) can be done by any Administrators-group user.`})]})]})]}),`\n`,_jsx(Heading,{level:`2`,id:`add-a-user-group`,children:`Add a user group`}),`\n`,_jsx(_components.p,{children:`User groups work the same way as users — same Endpoint Access, same Administrative Permissions, same User-to-User access mechanism. Users in a group inherit the group’s permissions.`}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`Open Add User Group`,children:_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`Users`}),` page, click `,_jsx(_components.strong,{children:`Add User Group`}),` in the top right.`]})}),_jsx(Step,{title:`Set group properties`,children:_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`Group Properties`}),` tab, enter a `,_jsx(_components.strong,{children:`Name`}),` (optionally a description), then click `,_jsx(_components.strong,{children:`Next`}),`.`]})}),_jsx(Step,{title:`Add members`,children:_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`Management Tool Users`}),` tab, click `,_jsx(_components.strong,{children:`Add Users`}),` in the top left, select the users to add, then click `,_jsx(_components.strong,{children:`Next`}),`.`]})}),_jsx(Step,{title:`Set administrative permissions`,children:_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`Administrative Permissions`}),` tab, select the `,_jsx(_components.a,{href:`/administration/users/administrative-permissions`,children:`administrative permissions`}),` all group members will inherit. Click `,_jsx(_components.strong,{children:`Next`}),`.`]})}),_jsx(Step,{title:`Set Endpoint access`,children:_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`Endpoint Access`}),` tab, for each Endpoint or Endpoint group, click the `,_jsx(_components.strong,{children:`Edit Permissions`}),` icon and select the `,_jsx(_components.a,{href:`/administration/users/client-permissions`,children:`Endpoint permissions`}),` to grant. Click `,_jsx(_components.strong,{children:`Save`}),` after each, then `,_jsx(_components.strong,{children:`Next`}),`.`]})}),_jsx(Step,{title:`(Optional) Set User-to-User access`,children:_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`User Access`}),` tab, restrict which endpoint users’ monitoring results group members can see — same mechanism as for individual users in `,_jsx(_components.a,{href:`#add-a-user`,children:`Add a user`}),`.`]})}),_jsx(Step,{title:`Finish`,children:_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Finish`}),`. The new user group appears on the Users page.`]})})]}),`\n`,_jsx(Heading,{level:`2`,id:`edit-a-user-group`,children:`Edit a user group`}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`Open the group`,children:_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`Users`}),` page, click the `,_jsx(_components.strong,{children:`Edit Group`}),` icon in the top right of the user group.`]})}),_jsx(Step,{title:`Make your changes`,children:_jsxs(_components.p,{children:[`Edit properties, members, permissions, and Endpoint access on the corresponding tabs — same as when `,_jsx(_components.a,{href:`#add-a-user-group`,children:`adding a user group`}),`.`]})}),_jsx(Step,{title:`Save`,children:_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Finish`}),` to save and exit, or `,_jsx(_components.strong,{children:`Next`}),` to save progressively.`]})})]}),`\n`,_jsx(Warning,{children:_jsxs(_components.p,{children:[`The default `,_jsx(_components.code,{children:`admin`}),` user can’t be removed from the `,_jsx(_components.strong,{children:`Administrators`}),` user group.`]})}),`\n`,_jsx(Heading,{level:`2`,id:`delete-a-user-group`,children:`Delete a user group`}),`\n`,_jsx(Warning,{children:_jsxs(_components.p,{children:[`Deleting a user group `,_jsx(_components.strong,{children:`doesn’t delete the users in it`}),` — but those users lose any permissions they inherited only from this group. Permissions inherited from other groups or assigned directly to the user remain.`]})}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`Open the group`,children:_jsxs(_components.p,{children:[`Click the `,_jsx(_components.strong,{children:`Edit Group`}),` icon in the top right of the user group on the Users page.`]})}),_jsx(Step,{title:`Delete`,children:_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`Group Properties`}),` tab, click `,_jsx(_components.strong,{children:`Delete Group`}),` at the bottom of the page.`]})}),_jsx(Step,{title:`Confirm`,children:_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Approve`}),` in the confirmation message.`]})})]}),`\n`,_jsx(Note,{children:_jsxs(_components.p,{children:[`The `,_jsx(_components.strong,{children:`All Users`}),` group can’t be deleted.`]})}),`\n`,_jsx(Heading,{level:`2`,id:`related`,children:`Related`}),`\n`,_jsxs(CardGroup,{cols:2,children:[_jsx(Card,{title:`Administrative permissions reference`,icon:`key`,href:`/administration/users/administrative-permissions`,children:_jsx(_components.p,{children:`The administrative permissions and what each one grants.`})}),_jsx(Card,{title:`Endpoint permissions reference`,icon:`lock`,href:`/administration/users/client-permissions`,children:_jsx(_components.p,{children:`The per-Endpoint permissions, plus a worked permission-inheritance example.`})}),_jsx(Card,{title:`Which sessions a user can see`,icon:`eye`,href:`/administration/users/session-visibility`,children:_jsx(_components.p,{children:`How administrative and Endpoint permissions combine to scope session access.`})}),_jsx(Card,{title:`Two-factor authentication`,icon:`smartphone`,href:`/administration/access/two-factor-authentication`,children:_jsx(_components.p,{children:`Configure 2FA across users and the deployment.`})}),_jsx(Card,{title:`ACB application accounts`,icon:`plug`,href:`/api/acb/overview`,children:_jsx(_components.p,{children:`Service-to-service authentication for the API.`})})]})]})}function MDXContent(props={}){const{wrapper:MDXLayout}={..._provideComponents(),...props.components};return MDXLayout?_jsx(MDXLayout,{...props,children:_jsx(_createMdxContent,{...props})}):_createMdxContent(props)}return{default:MDXContent};function _missingMdxReference(id,component){throw new Error(`Expected `+(component?`component`:`object`)+\" `\"+id+\"` to be defined: you likely forgot to import, pass, or provide it.\")}","frontmatter":{},"scope":{"codeStyling":"system","config":{},"pageMetadata":{"title":"Users and User Groups","sidebarTitle":"Users","description":"Syteca user management: three user types (internal, Active Directory, application account), five default user groups, custom groups, per-Endpoint permission scoping, two-factor authentication, and admin hardening.","icon":"users","keywords":["syteca user management","rbac pam platform","active directory user groups syteca","application account acb","user-to-user access","disable default admin","syteca 2fa"],"href":"/administration/users/users"}}},"mdxSourceWithNoJs":null},"mdxExtracts":{"tableOfContents":[{"title":"RBAC built for the people who run a PAM platform","slug":"rbac-built-for-the-people-who-run-a-pam-platform","depth":2,"children":[]},{"title":"The default admin and tenant model","slug":"the-default-admin-and-tenant-model","depth":2,"children":[]},{"title":"Three user types","slug":"three-user-types","depth":2,"children":[]},{"title":"Five default user groups","slug":"five-default-user-groups","depth":2,"children":[]},{"title":"Permission inheritance","slug":"permission-inheritance","depth":2,"children":[]},{"title":"Open the Users page","slug":"open-the-users-page","depth":2,"children":[]},{"title":"Add a user","slug":"add-a-user","depth":2,"children":[]},{"title":"Edit a user","slug":"edit-a-user","depth":2,"children":[]},{"title":"Lock and unlock users","slug":"lock-and-unlock-users","depth":2,"children":[]},{"title":"Delete a user","slug":"delete-a-user","depth":2,"children":[]},{"title":"Disable the default admin","slug":"disable-the-default-admin","depth":2,"children":[{"title":"Prerequisites","slug":"prerequisites","depth":3,"children":[]},{"title":"Disable the default admin","slug":"disable-the-default-admin-2","depth":3,"children":[]},{"title":"Restrictions after disabling","slug":"restrictions-after-disabling","depth":3,"children":[]}]},{"title":"Add a user group","slug":"add-a-user-group","depth":2,"children":[]},{"title":"Edit a user group","slug":"edit-a-user-group","depth":2,"children":[]},{"title":"Delete a user group","slug":"delete-a-user-group","depth":2,"children":[]},{"title":"Related","slug":"related","depth":2,"children":[]}],"codeExamples":{}},"jsLinks":[],"subdomain":"syteca","siteName":"Syteca","title":"Users and User Groups - Syteca","navMaps":{"firstHrefInVersion":{},"firstHrefInLanguage":{}},"lastModified":"2026-10-30T22:55:45.461Z","originalFileLocation":"administration/users/users.mdx"},"headHtml":"\u003cscript data-mint-head>(function(){var d=document.documentElement,p=null;if(!p){try{p=localStorage.getItem(\"isDarkMode\")}catch(e){}if(p==='true')p='dark';else if(p==='false')p='light';if(p!=='light'\u0026\u0026p!=='dark'\u0026\u0026p!=='system')p=\"system\"}var r=p==='system'?(matchMedia(\"(prefers-color-scheme: dark)\").matches?'dark':'light'):p;d.classList.remove(r==='dark'?'light':'dark');d.classList.add(r);d.setAttribute(\"data-theme-preference\",p)})();\u003c/script>\u003cmeta data-mint-head name=\"description\" content=\"Syteca user management: three user types (internal, Active Directory, application account), five default user groups, custom groups, per-Endpoint permission scoping, two-factor authentication, and admin hardening.\">\u003cmeta data-mint-head name=\"application-name\" content=\"Syteca\">\u003cmeta data-mint-head name=\"generator\" content=\"Mintlify\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon/android-chrome-192x192.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"apple-touch-icon\" type=\"image/png\" sizes=\"180x180\" href=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon/apple-touch-icon.png\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon/favicon-16x16.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon/favicon-32x32.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon/favicon.ico\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon-dark/android-chrome-192x192.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon-dark/favicon-16x16.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon-dark/favicon-32x32.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon-dark/favicon.ico\" media=\"(prefers-color-scheme: dark)\">\u003cmeta data-mint-head property=\"og:title\" content=\"Users and User Groups - Syteca\">\u003cmeta data-mint-head property=\"og:description\" content=\"Syteca user management: three user types (internal, Active Directory, application account), five default user groups, custom groups, per-Endpoint permission scoping, two-factor authentication, and admin hardening.\">\u003cmeta data-mint-head property=\"og:site_name\" content=\"Syteca Docs\">\u003cmeta data-mint-head property=\"og:url\" content=\"https://www.syteca.com/docs/administration/users/users\">\u003cmeta data-mint-head property=\"og:type\" content=\"website\">\u003cmeta data-mint-head property=\"og:image\" content=\"https://www.syteca.com/og-default.png\">\u003cmeta data-mint-head property=\"og:image:width\" content=\"1200\">\u003cmeta data-mint-head property=\"og:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"twitter:card\" content=\"summary_large_image\">\u003cmeta data-mint-head name=\"twitter:title\" content=\"Users and User Groups - Syteca\">\u003cmeta data-mint-head name=\"twitter:description\" content=\"Syteca user management: three user types (internal, Active Directory, application account), five default user groups, custom groups, per-Endpoint permission scoping, two-factor authentication, and admin hardening.\">\u003cmeta data-mint-head name=\"twitter:image\" content=\"https://www.syteca.com/og-default.png\">\u003cmeta data-mint-head name=\"twitter:image:width\" content=\"1200\">\u003cmeta data-mint-head name=\"twitter:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"msapplication-config\" content=\"/docs/mintlify-assets/_mintlify/favicons/syteca/6kVJ1RNAbG010Toj/_generated/favicon/browserconfig.xml\">\u003cmeta data-mint-head name=\"apple-mobile-web-app-title\" content=\"Syteca\">\u003cmeta data-mint-head name=\"msapplication-TileColor\" content=\"#2563EB\">\u003clink data-mint-head rel=\"canonical\" href=\"https://www.syteca.com/docs/administration/users/users\">\u003clink data-mint-head rel=\"alternate\" type=\"application/xml\" href=\"/docs/sitemap.xml\">\u003clink data-mint-head rel=\"alternate\" type=\"text/markdown\" href=\"/docs/administration/users/users.md\">\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@graph\":[{\"@type\":\"Organization\",\"@id\":\"https://www.syteca.com/#organization\",\"name\":\"Syteca\",\"url\":\"https://www.syteca.com\",\"logo\":{\"@type\":\"ImageObject\",\"url\":\"https://mintcdn.com/syteca/ZVta4JfIcSnC47NX/logo/syteca-light.svg?fit=max\u0026auto=format\u0026n=ZVta4JfIcSnC47NX\u0026q=85\u0026s=154a18f69aa4aefa55de0de7669934c7\"}},{\"@type\":\"WebSite\",\"@id\":\"https://www.syteca.com/docs#website\",\"name\":\"Syteca\",\"url\":\"https://www.syteca.com/docs\",\"publisher\":{\"@id\":\"https://www.syteca.com/#organization\"}},{\"@type\":\"WebPage\",\"@id\":\"https://www.syteca.com/docs/administration/users/users#webpage\",\"url\":\"https://www.syteca.com/docs/administration/users/users\",\"name\":\"Users and User Groups\",\"description\":\"Syteca user management: three user types (internal, Active Directory, application account), five default user groups, custom groups, per-Endpoint permission scoping, two-factor authentication, and admin hardening.\",\"dateModified\":\"2026-10-30T22:55:45.461Z\",\"isPartOf\":{\"@id\":\"https://www.syteca.com/docs#website\"},\"breadcrumb\":{\"@id\":\"https://www.syteca.com/docs/administration/users/users#breadcrumb\"}},{\"@type\":\"BreadcrumbList\",\"@id\":\"https://www.syteca.com/docs/administration/users/users#breadcrumb\",\"itemListElement\":[{\"@type\":\"ListItem\",\"position\":1,\"name\":\"Syteca\",\"item\":\"https://www.syteca.com/docs\"},{\"@type\":\"ListItem\",\"position\":2,\"name\":\"Users and User Groups\",\"item\":\"https://www.syteca.com/docs/administration/users/users\"}]},{\"@type\":[\"Article\",\"TechArticle\"],\"@id\":\"https://www.syteca.com/docs/administration/users/users#article\",\"headline\":\"Users and User Groups\",\"name\":\"Users and User Groups\",\"description\":\"Syteca user management: three user types (internal, Active Directory, application account), five default user groups, custom groups, per-Endpoint permission scoping, two-factor authentication, and admin hardening.\",\"url\":\"https://www.syteca.com/docs/administration/users/users\",\"mainEntityOfPage\":{\"@id\":\"https://www.syteca.com/docs/administration/users/users#webpage\"},\"image\":\"https://www.syteca.com/og-default.png\",\"dateModified\":\"2026-10-30T22:55:45.461Z\",\"keywords\":\"syteca user management, rbac pam platform, active directory user groups syteca, application account acb, user-to-user access, disable default admin, syteca 2fa\",\"publisher\":{\"@id\":\"https://www.syteca.com/#organization\"},\"isPartOf\":{\"@id\":\"https://www.syteca.com/docs#website\"}}]}\u003c/script>\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@type\":\"WebSite\",\"name\":\"Syteca\",\"creator\":{\"@type\":\"Organization\",\"name\":\"Mintlify\",\"url\":\"https://mintlify.com\"}}\u003c/script>","siteName":"Syteca","nav":{"global":null,"tabs":[{"tab":"Get Started","pages":[{"title":"Get Started","href":"/get-started/what-is-syteca"}]},{"tab":"Session Monitoring","pages":[{"title":"Session Monitoring","href":"/session-monitoring/overview"}]},{"tab":"Privileged Access Management","pages":[{"title":"Privileged Access Management","href":"/pam/overview"}]},{"tab":"Endpoint Risk Control","pages":[{"title":"Endpoint Risk Control","href":"/risk/overview"}]},{"tab":"Administration","groups":[{"group":"Overview","pages":[{"title":"Administration","sidebarTitle":"Overview","icon":"settings","href":"/administration/overview"}]},{"group":"Installation","pages":[{"title":"Syteca Architecture","sidebarTitle":"Architecture","icon":"layers","href":"/administration/deployment/architecture"},{"title":"Comparison of Standard and High Availability Modes","sidebarTitle":"Standard vs HA Modes","icon":"scale","href":"/administration/deployment/standard-vs-ha-modes"},{"title":"Installation Checklist","sidebarTitle":"Installation checklist","icon":"list-checks","href":"/administration/deployment/installation-checklist"},{"title":"Install the Application Server","sidebarTitle":"Install Application Server","icon":"server","href":"/administration/deployment/install-application-server"},{"title":"The Syteca Server Tray Application","sidebarTitle":"Server Tray Application","icon":"server","href":"/administration/deployment/server-tray-application"},{"title":"Application Server Advanced Settings","sidebarTitle":"Advanced settings","icon":"settings","href":"/administration/deployment/server-advanced-settings"},{"title":"Management Tool Prerequisites","sidebarTitle":"Management Tool prerequisites","icon":"list-checks","href":"/administration/deployment/management-tool-prerequisites"},{"title":"Install the Management Tool","sidebarTitle":"Install Management Tool","icon":"download","href":"/administration/deployment/install-management-tool"},{"title":"Install the Syteca Tray Notifications Application","sidebarTitle":"Tray Notifications","icon":"bell-off","href":"/administration/deployment/tray-notifications"},{"title":"Update the Application Server","sidebarTitle":"Update Application Server","icon":"arrow-up","href":"/administration/deployment/update-application-server"},{"title":"Update Syteca","sidebarTitle":"Update Syteca","icon":"arrow-up","href":"/administration/deployment/update-syteca"},{"title":"Uninstall the Application Server","sidebarTitle":"Uninstall Application Server","icon":"trash-2","href":"/administration/deployment/uninstall-application-server"},{"title":"Migrate the Application Server to Another Computer","sidebarTitle":"Migrate Application Server","icon":"server","href":"/administration/deployment/migrate-application-server"}]},{"group":"Scaling \u0026 High Availability","pages":[{"title":"High Availability, Load Balancing, and Disaster Recovery","sidebarTitle":"High Availability","icon":"network","href":"/administration/deployment/high-availability"},{"title":"Deploy Syteca in a Microsoft Failover Cluster","sidebarTitle":"Failover cluster HA","icon":"server-cog","href":"/administration/deployment/failover-cluster-ha"},{"title":"Configure Golden Image Mode","sidebarTitle":"Golden Image Mode","icon":"copy","href":"/administration/deployment/golden-image-mode"},{"title":"VDI Monitoring","sidebarTitle":"VDI monitoring","icon":"monitor","href":"/administration/deployment/vdi-monitoring"},{"title":"Install the Syteca Master Panel","sidebarTitle":"Master Panel","icon":"monitor-check","href":"/administration/deployment/master-panel"},{"title":"Install Additional Application Servers for Load Balancing","sidebarTitle":"Load balancing install","icon":"server-cog","href":"/administration/deployment/load-balancing-installation"},{"title":"Shared Storage High Availability","sidebarTitle":"Shared Storage HA","icon":"hard-drive","href":"/administration/deployment/shared-storage-ha"},{"title":"Deploy Syteca on Azure Cloud from Azure Marketplace","sidebarTitle":"Azure Marketplace","icon":"cloud","href":"/administration/deployment/azure-marketplace"}]},{"group":"Database","pages":[{"title":"Database Management","sidebarTitle":"Database management","icon":"database","href":"/administration/deployment/database-management"},{"title":"MS SQL vs PostgreSQL for Syteca","sidebarTitle":"Compare Database Types","icon":"database","href":"/administration/database/compare-databases"},{"title":"Edit the Database Parameters","sidebarTitle":"Database Parameters","icon":"database","href":"/administration/database/database-parameters"},{"title":"Creating Databases Manually","sidebarTitle":"Creating Databases Manually","icon":"database","href":"/administration/database/creating-databases-manually"},{"title":"Set Up a Remote PostgreSQL Server","sidebarTitle":"Remote PostgreSQL Setup","icon":"network","href":"/administration/database/postgresql-remote"},{"title":"Moving the MS SQL Database","sidebarTitle":"Moving the MS SQL Database","icon":"database","href":"/administration/database/moving-ms-sql-database"},{"title":"Moving the PostgreSQL Database","sidebarTitle":"Moving the PostgreSQL Database","icon":"database","href":"/administration/database/moving-postgresql-database"},{"title":"MS SQL Database Maintenance: Index Rebuilding","sidebarTitle":"MS SQL Index Maintenance","icon":"database","href":"/administration/database/ms-sql-index-maintenance"},{"title":"Using a gMSA or sMSA Account for the MS SQL Server Connection","sidebarTitle":"gMSA/sMSA Account","icon":"shield-check","href":"/administration/database/gmsa-account"},{"title":"Configure Windows Authentication for Use with NTLM","sidebarTitle":"Windows Authentication \u0026 NTLM","description":"Prevent authentication errors when Windows Authentication uses the NTLM security protocol to connect to an MS SQL Server database with NTLM restrictions in place.","icon":"shield","href":"/administration/database/windows-authentication-ntlm"}]},{"group":"Users and Permissions","pages":[{"title":"Users and User Groups","sidebarTitle":"Users","icon":"users","href":"/administration/users/users"},{"title":"Administrative Permissions","sidebarTitle":"Administrative permissions","description":"Reference for Syteca's administrative permissions — what each one grants, prerequisites, and the actions it unlocks on the Users page, Configuration, dashboards, and reports.","icon":"key","href":"/administration/users/administrative-permissions"},{"title":"Endpoint Permissions","sidebarTitle":"Endpoint permissions","icon":"lock","href":"/administration/users/client-permissions"},{"title":"Which Sessions a User Can See","sidebarTitle":"Session visibility","icon":"eye","href":"/administration/users/session-visibility"}]},{"group":"Clients","pages":[{"title":"The Clients Page","sidebarTitle":"Overview","icon":"server","href":"/administration/clients/overview"},{"title":"Windows Client Installation Prerequisites","sidebarTitle":"Windows install prerequisites","icon":"monitor-check","href":"/administration/clients/windows-install-prerequisites"},{"title":"Windows Client Installation Package Parameters","sidebarTitle":"Installation Package Parameters","icon":"file-cog","href":"/administration/clients/windows-installation-package-parameters"},{"title":"Windows Clients","sidebarTitle":"Windows Clients","icon":"monitor","href":"/administration/clients/windows"},{"title":"Install Windows Clients","sidebarTitle":"Install Windows Clients","icon":"monitor-down","href":"/administration/clients/install-windows"},{"title":"Deploy the Windows Client Using Microsoft Intune","sidebarTitle":"Intune Deployment","icon":"windows","href":"/administration/clients/windows-intune-deployment"},{"title":"Editing the Windows Client Configuration","sidebarTitle":"Editing Client Configuration","icon":"sliders-horizontal","href":"/administration/clients/windows-client-configuration"},{"title":"macOS Clients","sidebarTitle":"macOS Clients","icon":"apple","href":"/administration/clients/macos"},{"title":"macOS Hidden Client","sidebarTitle":"macOS Hidden Client","icon":"eye-off","href":"/administration/clients/macos-hidden"},{"title":"Install macOS Clients","sidebarTitle":"Install macOS Clients","icon":"apple","href":"/administration/clients/install-macos"},{"title":"Linux Clients","sidebarTitle":"Linux Clients","icon":"terminal","href":"/administration/clients/linux"},{"title":"Install Linux Clients","sidebarTitle":"Install Linux Clients","icon":"terminal","href":"/administration/clients/install-linux"},{"title":"Client Groups","sidebarTitle":"Client groups","icon":"server-cog","href":"/administration/clients/client-groups"},{"title":"Update Clients","sidebarTitle":"Update Clients","icon":"refresh-cw","href":"/administration/clients/update-clients"},{"title":"Uninstall Clients","sidebarTitle":"Uninstall Clients","icon":"trash-2","href":"/administration/clients/uninstall"},{"title":"Delete Clients","sidebarTitle":"Delete Clients","icon":"trash-2","href":"/administration/clients/delete-clients"},{"title":"Offline Cache Size Parameter","sidebarTitle":"Offline Cache Size","icon":"database","href":"/administration/clients/parameters/offline-cache-size"}]},{"group":"Access","pages":[{"title":"Endpoint Access Control","sidebarTitle":"Endpoint access control","icon":"shield-check","href":"/administration/access/endpoint-access-control"},{"title":"Smart Card Access","sidebarTitle":"Smart card access","icon":"id-card","href":"/administration/access/smart-card-access"},{"title":"Two-Factor Authentication","sidebarTitle":"Two-factor authentication","icon":"smartphone","href":"/administration/access/two-factor-authentication"}]},{"group":"Management Tool Settings","pages":[{"title":"System Settings","sidebarTitle":"System Settings","icon":"settings","href":"/administration/configuration/system-settings"},{"title":"Email Sending Settings","sidebarTitle":"Email Sending Settings","icon":"mail","href":"/administration/configuration/email-sending-settings"},{"title":"Customization Settings","sidebarTitle":"Customization Settings","icon":"palette","href":"/administration/configuration/customization-settings"},{"title":"Date \u0026 Time Format Settings","sidebarTitle":"Date \u0026 Time Format","icon":"calendar-clock","href":"/administration/configuration/date-time-format"},{"title":"Export Storage Settings","sidebarTitle":"Export Storage Settings","icon":"folder","href":"/administration/configuration/export-storage-settings"},{"title":"Database Management Settings","sidebarTitle":"Database Management Settings","icon":"database","href":"/administration/configuration/database-management-settings"},{"title":"Account Discovery Settings","sidebarTitle":"Account Discovery Settings","icon":"settings","href":"/administration/configuration/account-discovery-settings"}]},{"group":"Client Parameters","pages":[{"title":"Endpoint Description","sidebarTitle":"Endpoint description","icon":"tag","href":"/administration/clients/parameters/client-description"},{"title":"Update Client Automatically","sidebarTitle":"Update client automatically","icon":"refresh-ccw","href":"/administration/clients/parameters/update-client-automatically"},{"title":"Disconnected Endpoint Detection","sidebarTitle":"Disconnected endpoint detection","icon":"bell-off","href":"/administration/clients/parameters/disconnected-client-detection"},{"title":"Auto-Cleanup Parameters","sidebarTitle":"Auto-cleanup","icon":"trash","href":"/administration/clients/parameters/auto-cleanup"},{"title":"Protected Mode","sidebarTitle":"Protected mode","icon":"shield-check","href":"/administration/clients/parameters/protected-mode"},{"title":"Syteca PAM Connection Manager (Jump Server Mode)","sidebarTitle":"PAM Connection Manager","icon":"arrow-right-left","href":"/administration/clients/parameters/pam-connection-manager"},{"title":"Windows Event Log Integration","sidebarTitle":"Windows Event Log integration","icon":"scroll-text","href":"/administration/clients/parameters/windows-event-log-integration"},{"title":"Custom Path for the Client Installation Folder","sidebarTitle":"Custom installation path","icon":"folder-cog","href":"/administration/clients/parameters/custom-installation-path"},{"title":"One-Time Passwords","sidebarTitle":"One-Time Passwords","icon":"key-round","href":"/administration/clients/parameters/one-time-passwords"},{"title":"Secondary User Authentication","sidebarTitle":"Secondary User Authentication","icon":"user-check","href":"/administration/clients/parameters/secondary-user-authentication"},{"title":"Display an Additional Message on Login","sidebarTitle":"Additional Login Message","icon":"message-square-warning","href":"/administration/clients/parameters/additional-login-message"},{"title":"Linux Client Parameters","sidebarTitle":"Linux Client Parameters","icon":"terminal","href":"/administration/clients/parameters/linux-client-parameters"}]},{"group":"Licensing","pages":[{"title":"Licensing Overview","sidebarTitle":"Overview","icon":"key","href":"/administration/licensing/overview"},{"title":"Activate or Update the Serial Key","sidebarTitle":"Activate serial key","icon":"key-round","href":"/administration/licensing/activate-serial-key"},{"title":"Manage the Serial Key","sidebarTitle":"Manage serial key","icon":"key-round","href":"/administration/licensing/manage-serial-key"},{"title":"Assign PAM Seat Licenses","sidebarTitle":"Assign PAM seat licenses","icon":"users","href":"/administration/licensing/assign-pam-seat-licenses"},{"title":"Assign Endpoint Licenses to Endpoints","sidebarTitle":"Manual endpoint licenses assignment","icon":"laptop","href":"/administration/licensing/assign-endpoint-licenses"},{"title":"Automatic License Assignment","sidebarTitle":"Automatic endpoint license assignment","icon":"list-ordered","href":"/administration/licensing/automatic-license-assignment"}]},{"group":"Multi-Tenant","pages":[{"title":"Multi-Tenant Mode","sidebarTitle":"Overview","icon":"users-round","href":"/administration/multi-tenant/overview"},{"title":"Manage Tenants","sidebarTitle":"Manage tenants","icon":"list-tree","href":"/administration/multi-tenant/manage-tenants"},{"title":"Cross-Tenant Access","sidebarTitle":"Cross-tenant access","icon":"user-plus","href":"/administration/multi-tenant/cross-tenant-access"}]},{"group":"Dashboards","pages":[{"title":"Application Server Resource Monitoring","sidebarTitle":"AS resource monitoring","icon":"chart-line","href":"/administration/dashboards/application-server-monitoring"},{"title":"System Health Dashboards","sidebarTitle":"System health dashboards","icon":"activity","href":"/administration/dashboards/system-health-dashboards"},{"title":"System Error and Warning Reference","sidebarTitle":"Error Reference","icon":"search-alert","href":"/administration/dashboards/system-error-reference"}]},{"group":"Audit Log","pages":[{"title":"Audit Log","sidebarTitle":"Audit log","icon":"scroll-text","href":"/administration/audit-log"}]},{"group":"Security","pages":[{"title":"Syteca Encryption","sidebarTitle":"Encryption","icon":"lock","href":"/administration/security/encryption"},{"title":"Master Certificate Management","sidebarTitle":"Master Certificate","icon":"key","href":"/administration/security/master-certificate"},{"title":"Third-Party Software Used by Syteca","sidebarTitle":"Third-Party Software","icon":"package","href":"/administration/security/third-party-notices"},{"title":"Add IIS Request Filtering Exceptions for Syteca","sidebarTitle":"IIS Request Filtering","icon":"shield-check","href":"/administration/security/iis-request-filtering"},{"title":"Exclude Syteca Processes from Antivirus Software","sidebarTitle":"Antivirus Exclusions","icon":"shield-check","href":"/administration/security/antivirus-exclusions"},{"title":"Keystroke Logging and Password Masking","sidebarTitle":"Keystroke \u0026 Password Masking","icon":"eye-off","href":"/administration/security/keystroke-password-masking"},{"title":"Move the Master Certificate to Thales HSM","sidebarTitle":"Thales HSM Integration","icon":"shield-check","href":"/administration/integrations/thales-hsm"}]}]},{"tab":"API \u0026 Integrations","pages":[{"title":"API \u0026 Integrations","href":"/api/overview"}]},{"tab":"Release Notes","pages":[{"title":"Release Notes","href":"/release-notes/overview"}]},{"tab":"Resources","pages":[{"title":"Resources","href":"/resources/overview"}]}]},"basePath":"","title":"Users and User Groups - Syteca","buildId":"dpl_Acry4NrQAgjcikyFgVE2eJ7XQCAv","deploymentId":"dpl_Acry4NrQAgjcikyFgVE2eJ7XQCAv","dynamics":["07c022d89b","a74be98ba7"],"chunks":["Frame-D9VvKFqQ.js","DynamicMarkdown-BCpKo5ib.js","zoom-image-lightbox-DBRtNxbY.js","lightbox-handle-r17bVUz3.js"]}